

Instant Download MS-100 Dumps Q&As Provide PDF&Test Engine
Fast Exam Updates MS-100 dumps with PDF Test Engine Practice
What Are The Job Prospects Of Microsoft MS-100 Exam?
Passing the Microsoft MS-100 exam and earning the associated certification demands tons of effort. But, it reaps enough and satisfactory outputs as well. The IT job market has a huge demand for Microsoft certified professionals. The way this test helps a candidate to get hold over high-end knowledge associated with evaluating, planning, deploying, migrating, and managing the Microsoft 365 services is laudable.
MS-100 verifies one's competence to handle the identity, compliance, security, and supporting technology-related tasks with full perfection. All these skills are ideal for job roles like Enterprise System Administrator and System Engineer. Both of these positions allow earning a handsome salary. As per the PayScale, the average pay for the mentioned professionals is $65k and $78k per year, respectively, which is just an average amount.
The Microsoft MS-100 exam covers a range of topics related to Microsoft 365 identity and services. This includes understanding key features and functionality of Microsoft 365, managing user identity and roles, implementing security and compliance features, and managing Microsoft 365 services. The exam also covers topics related to implementing and managing Microsoft 365 hybrid scenarios.
NEW QUESTION # 99
You need to create the UserLicenses group. The solution must meet the security requirements.
Which group type and control method should you use? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.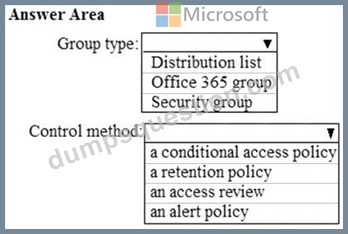
Answer:
Explanation:
Explanation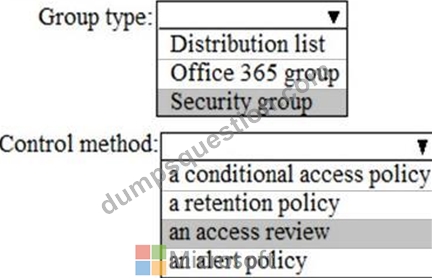
NEW QUESTION # 100
Your network contains an Active Directory domain and a Microsoft Azure Active Directory (Azure AD) tenant.
You implement directory synchronization for all 10.000 users in the organization.
You automate the creation of 100 new user accounts.
You need to ensure that the new user accounts synchronize to Azure AD as quickly as possible Which command should you run? To answer, select the appropriate options in the answer area.
NOTE: Each correct select ion is worth one point.
Answer:
Explanation:
Explanation
NEW QUESTION # 101
You have several Microsoft SharePoint document libraries in your on-premises environment.
You have a Microsoft 365 tenant that has directory synchronization implemented.
You plan to move all the document libraries to SharePoint Online.
You need to recommend a migration strategy for the document libraries.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation:
Explanation
The SharePoint Migration Tool lets you migrate content to SharePoint Online and OneDrive from the following locations:
* SharePoint Server 2013
* SharePoint Server 2010
* Network and local file shares
The first step is to create new SharePoint sites in SharePoint online. These sites will host the document libraries which will host the migrated content.
The second step is to create the document libraries in the SharePoint sites to host the migrated content.
The final step is to use the SharePoint Migration Tool to migrate the content.
Reference:
https://docs.microsoft.com/en-us/sharepointmigration/how-to-use-the-sharepoint-migration-tool
NEW QUESTION # 102
Your network contains a single Active Directory domain and two Microsoft Azure Active Directory (Azure AD) tenants.
You plan to implement directory synchronization for both Azure AD tenants. Each tenant will contain some of the Active Directory users.
You need to recommend a solution for the planned directory synchronization.
What should you include in the recommendation?
- A. Deploy one server that runs Azure AD Connect, and then specify two sync groups.
- B. Deploy one server that runs Azure AD Connect, and then filter the users for each tenant by using organizational unit (OU)-based filtering.
- C. Deploy two servers that run Azure AD Connect, and then filter the users for each tenant by using organizational unit (OU)-based filtering.
- D. Deploy one server that runs Azure AD Connect, and then filter the users for each tenant by using domain- based filtering.
Answer: C
Explanation:
There's a 1:1 relationship between an Azure AD Connect sync server and an Azure AD tenant. For each Azure AD tenant, you need one Azure AD Connect sync server installation.
Therefore, we need to deploy two servers that run Azure AD Connect for the two Azure AD tenants.
Each user account can only be synchronized to one Azure AD tenant. Therefore, we need a way of splitting the users between the two Azure AD tenants. Azure AD Connect offers three ways to filter which users get synchronized to an Azure AD tenant. You can use domain-based filtering if you have multiple domains in a forest, attribute-based filtering or OU-based filtering.
Note:
Other incorrect answers for this question include:
1. Deploy one server that runs Azure AD Connect, and then filter the users for each tenant by using attribute- based filtering.
2. Deploy one server that runs Azure AD Connect, and then specify two sync groups.
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/hybrid/plan-connect-topologies#multiple-azure-ad- tenants
https://docs.microsoft.com/en-us/azure/active-directory/hybrid/how-to-connect-sync-configure-filtering Manage User Identity and Roles Testlet 2 Case study This is a case study. Case studies are not timed separately. You can use as much exam time as you would like to complete each case. However, there may be additional case studies and sections on this exam. You must manage your time to ensure that you are able to complete all questions included on this exam in the time provided.
To answer the questions included in a case study, you will need to reference information that is provided in the case study. Case studies might contain exhibits and other resources that provide more information about the scenario that is described in the case study. Each question is independent of the other questions in this case study.
At the end of this case study, a review screen will appear. This screen allows you to review your answers and to make changes before you move to the next section of the exam. After you begin a new section, you cannot return to this section.
To start the case study
To display the first question in this case study, click the Next button. Use the buttons in the left pane to explore the content of the case study before you answer the questions. Clicking these buttons displays information such as business requirements, existing environment, and problem statements. When you are ready to answer a question, click the Question button to return to the question.
Overview
Contoso, Ltd. is a consulting company that has a main office in Montreal and two branch offices in Seattle and New York.
The offices have the users and devices shown in the following table.
Contoso recently purchased a Microsoft 365 E5 subscription.
Existing Environment
The network contains an Active directory forest named contoso.com and a Microsoft Azure Active Directory (Azure AD) tenant named contoso.onmicrosoft.com.
You recently configured the forest to sync to the Azure AD tenant.
You add and then verify adatum.com as an additional domain name.
All servers run Windows Server 2016.
All desktop computers and laptops run Windows 10 Enterprise and are joined to contoso.com.
All the mobile devices in the Montreal and Seattle offices run Android. All the mobile devices in the New York office run iOS.
Contoso has the users shown in the following table.
Contoso has the groups shown in the following table.
Microsoft Office 365 licenses are assigned only to Group2.
The network also contains external users from a vendor company who have Microsoft accounts that use a suffix of @outlook.com.
Requirements
Planned Changes
Contoso plans to provide email addresses for all the users in the following domains:
* East.adatum.com
* Contoso.adatum.com
* Humongousinsurance.com
Technical Requirements
Contoso identifies the following technical requirements:
* All new users must be assigned Office 365 licenses automatically.
* The principle of least privilege must be used whenever possible.
Security Requirements
Contoso identifies the following security requirements:
* Vendors must be able to authenticate by using their Microsoft account when accessing Contoso resources.
* User2 must be able to view reports and schedule the email delivery of security and compliance reports.
* The members of Group1 must be required to answer a security question before changing their password.
* User3 must be able to manage Office 365 connectors.
* User4 must be able to reset User3 password.
NEW QUESTION # 103
You are developing a new Microsoft Teams app that will contain the following functionality:
* Start a new chat
* Prompt users to install an app.
* Make a Microsoft Graph API call.
* Trigger a search-based command.
Which two functionalities can be implemented by using a deep link? Each correct answer presents part of the solution. NOTE: Each correct selection is worth one point
- A. Prompt users to install an app.
- B. Start a new chat
- C. Trigger a search-based command.
- D. Make a Microsoft Graph API call.
Answer: A,B
NEW QUESTION # 104
Which migration solution should you recommend for Project1?
- A. From the Exchange admin center, start a migration and select Remote move migration
- B. From Exchange Online PowerShell, run the New-MaiboxImportRequest cmdlet.
- C. From the Microsoft 365 admin center, start a data migration and click Upload PSST as the data service.
- D. From Exchange Online PowerShell, run the New-MaiboxExportRequest cmdlet.
Answer: A
NEW QUESTION # 105
You have a multitenant app named App1.
You need to ensure that App1 supports token acquisition when a user accesses the app by using a web browser that has a popup blocker extension enabled. How should you complete the Microsoft Authentication Library (MSAL) for JavaScript v2.0 code? To answer, select the appropriate options m the answer are a.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 106
Your company has a hybrid deployment of Microsoft 365.
An on-premises user named User1 is synced to Microsoft Azure Active Directory (Azure AD).
Azure AD Connect is configured as shown in the following exhibit.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
User1 cannot change her password from any Microsoft portals because Password Writeback is disabled in the Azure AD Connect configuration.
If the password for User1 is changed in Active Directory, the password will be synchronized to Azure AD because Password Synchronization is enabled in the Azure AD Connect configuration.
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/hybrid/how-to-connect-install-custom
NEW QUESTION # 107
You have a Microsoft 365 subscription.
From the Microsoft 365 admin center, you open the Microsoft 365 Apps usage report as shown in the following exhibit.
You need ensure that the report meets the following requirements:
* The Username column must display the actual name of each user.
* Usage of the Microsoft Teams mobile app must be displayed.
What should you modify for each requirement? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation: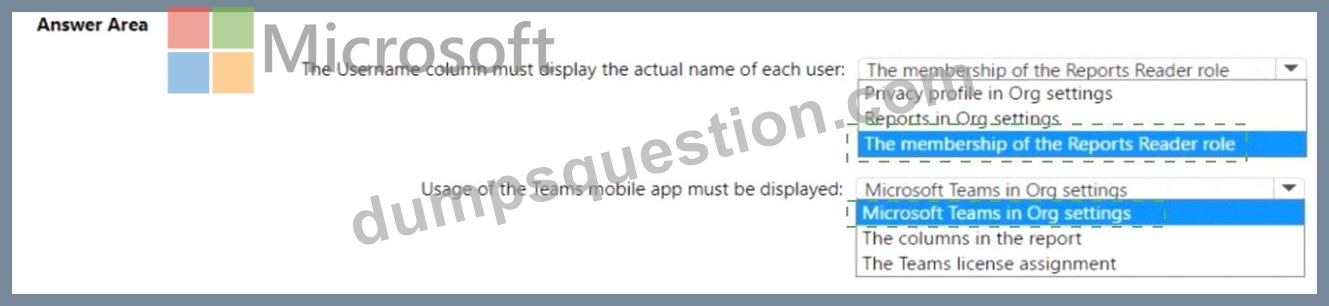
Explanation
NEW QUESTION # 108
You have a Microsoft Azure Active Directory (Azure AD) tenant that contains the users shown in the following table.
Your company uses Windows Defender Advanced Threat Protection (ATP). Windows Defender ATP contains the roles shown in the following table.
Windows Defender ATP contains the device groups shown in the following table.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation: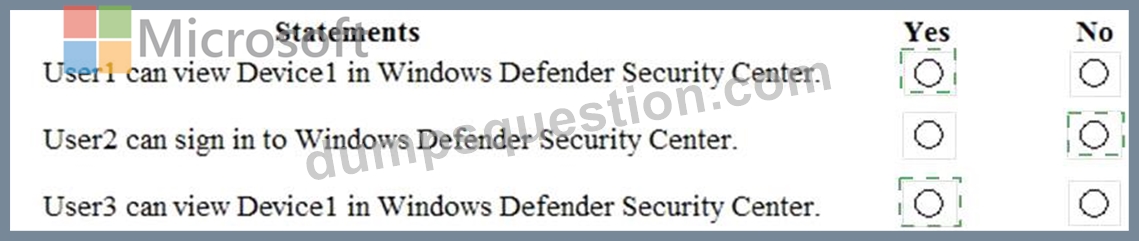
Explanation
NEW QUESTION # 109
You have a Microsoft Azure Active Directory (Azure AD) tenant.
Your company implements Windows Information Protection (WIP).
You need to modify which users and applications are affected by WIP.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.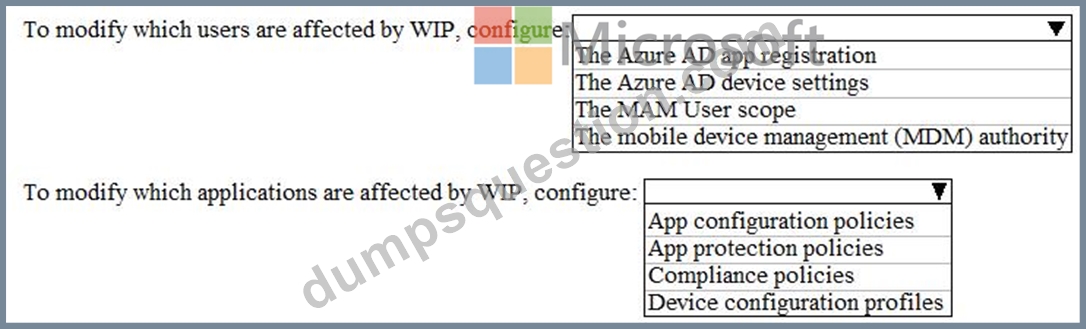
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/windows/security/information-protection/windows-information-protection/create-wip-policy-using-intune-azure
NEW QUESTION # 110
You have a new Microsoft 365 subscription.
A user named User1 has a mailbox in Microsoft Exchange Online.
You need to log any changes to the mailbox folder permissions of User1.
Which command should you run? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
To enable auditing for a single mailbox (in this example, belonging to Holly Sharp), use this PowerShell command: Set-Mailbox username -AuditEnabled $true References:
https://support.microsoft.com/en-us/help/4026501/office-auditing-in-office-365-for-admins
https://docs.microsoft.com/en-us/powershell/module/exchange/mailboxes/set-mailbox?view=exchange-ps
NEW QUESTION # 111
You need to meet the technical requirements for the user licenses.
Which two properties should you configure for each user? To answer, select the appropriate properties in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation: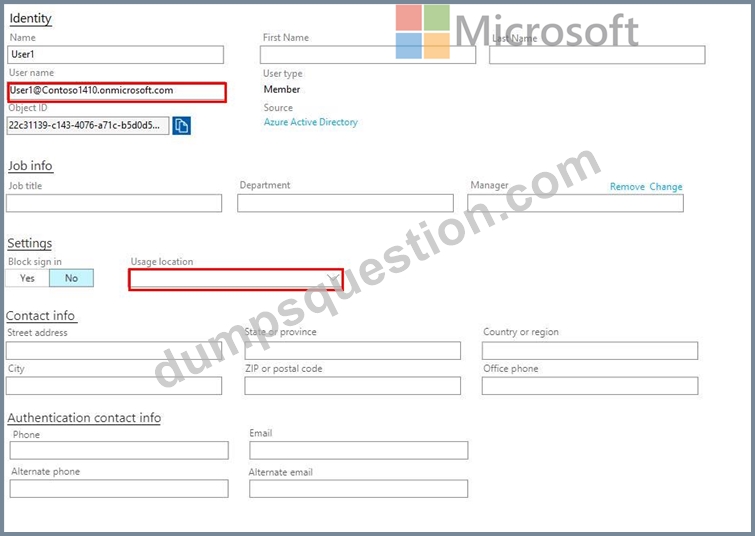
NEW QUESTION # 112
Please wait while the virtual machine loads. Once loaded, you may proceed to the lab section. This may take a few minutes, and the wait time will not be deducted from your overall test time.
When the Next button is available, click it to access the lab section. In this section, you will perform a set of tasks in a live environment. While most functionality will be available to you as it would be in a live environment, some functionality (e.g., copy and paste, ability to navigate to external websites) will not be possible by design.
Scoring is based on the outcome of performing the tasks stated in the lab. In other words, it doesn't matter how you accomplish the task, if you successfully perform it, you will earn credit for that task.
Labs are not timed separately, and this exam may have more than one lab that you must complete. You can use as much time as you would like to complete each lab. But, you should manage your time appropriately to ensure that you are able to complete the lab(s) and all other sections of the exam in the time provided.
Please note that once you submit your work by clicking the Next button within a lab, you will NOT be able to return to the lab.
You may now click next to proceed to the lab.
Lab information
Use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password, place your cursor in the Enter password box and click on the password below.
Microsoft 365 Username: [email protected]
Microsoft 365 Password: m3t^We$Z7&xy
If the Microsoft 365 portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support purposes only:
Lab Instance: 11440873
You need to create a SharePoint site named Project1. Users from your organization must be able to share content from the site to external users.
To answer, sign in to the Microsoft 365 portal.
Answer:
Explanation:
See explanation below.
Explanation
You need to create a SharePoint site and configure the sharing settings.
1. Go to the SharePoint Admin Center.
2. In the left navigation pane, expand Sites then select 'Active Sites'.
3. Click on the '+ Create' link to add a new site.
4. Select 'Other Options' then 'Team Site' for the template.
5. Give the site the name 'Project1'.
6. In the 'Primary Administrator' field, start typing 'admin' then select the [email protected] account when it appears.
7. Click Finish to create the site.
8. In the Active Sites list, select the Project1 site.
9. Click the Sharing link at the top of the sites list.
10. Under 'External Sharing', select 'Anyone'.
11. Click Save to save the changes.
NEW QUESTION # 113
You have a Microsoft 365 subscription that contains the users shown in the following table.
You have the named locations shown in the following table.
You create a conditional access policy that has the following configurations:
Users and groups:
Include: Group1
Exclude: Group2
Cloud apps: Include all cloud apps
Conditions:
Include: Any location
Exclude: Montreal
Access control: Grant access, Require multi-factor authentication
User1 is on the multi-factor authentication (MFA) blocked users list.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/authentication/howto-mfa-mfasettings
NEW QUESTION # 114
You have an app that uses the Microsoft Graph API. The app will perform the following actions m sequence:
* Update a user's city to Redmond.
* Retrieve the current user s profile.
You need to implement batching for the app
Which HTTP methods should you use in the batch request? To answer, select the appropriate options in the answer area NOTE: Each correct selection is worth one point.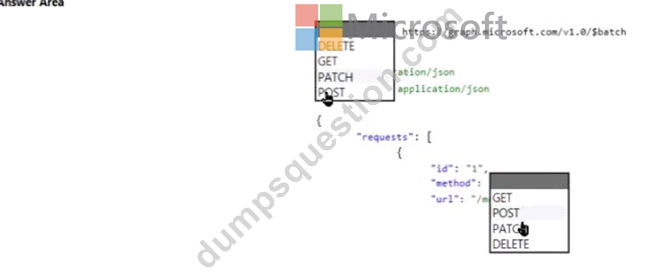
Answer:
Explanation: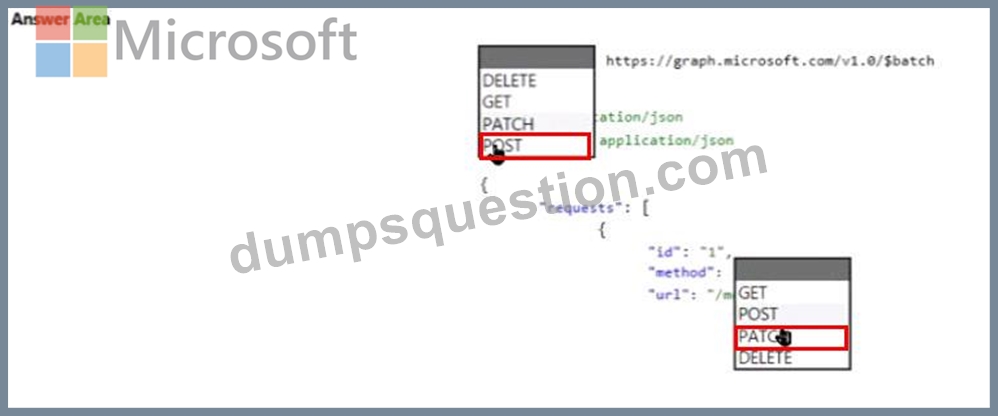
NEW QUESTION # 115
You have a Microsoft 365 subscription that contains a Microsoft Azure Active Directory (Azure AD) tenant named contoso.com. The tenant includes a user named User1 You enable Azure AD Identity Protection.
You need to ensure that User1 can review the list in Azure AD Identity Protection of users nagged for risk.
The solution must use the principle of least privilege.
To which role should you add User1?
- A. Global administrator
- B. Compliance administrator
- C. Reports reader
- D. Security reader
Answer: B
NEW QUESTION # 116
Your network contains an Active Directory forest named contoso.local.
You purchase a Microsoft 365 subscription.
You plan to move to Microsoft and to implement a hybrid deployment solution for the next 12 months.
You need to prepare for the planned move to Microsoft 365.
What is the best action to perform before you implement directory synchronization? More than one answer choice may achieve the goal. Select the BEST answer.
- A. Rename the Active Directory forest.
- B. Purchase a custom domain name.
- C. Purchase a third-party X.509 certificate.
- D. Create an external forest trust.
Answer: B
Explanation:
The first thing you need to do before you implement directory synchronization is to purchase a custom domain name. This could be the domain name that you use in your on-premise Active Directory if it's a routable domain name, for example, contoso.com.
If you use a non-routable domain name in your Active Directory, for example contoso.local, you'll need to add the routable domain name as a UPN suffix in Active Directory.
Reference:
https://docs.microsoft.com/en-us/office365/enterprise/set-up-directory-synchronization
NEW QUESTION # 117
Your network contains an on-premises Active Directory domain.
You have a Microsoft 365 subscription.
You implement a directory synchronization solution that uses pass-through authentication.
You configure Microsoft Azure Active Directory (Azure AD) smart lockout as shown in the following exhibit.
You discover that Active Directory users can use the passwords in the custom banned passwords list.
You need to ensure that banned passwords are effective for all users.
Which three actions should you perform? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
- A. From Custom banned passwords, modify the Enforce custom list setting.
- B. From a domain controller, install the Microsoft AAD Application Proxy connector.
- C. From Active Directory, modify the Default Domain Policy.
- D. From all the domain controllers, install the Azure AD Password Protection DC Agent.
- E. From a domain controller, install the Azure AD Password Protection Proxy.
- F. From Password protection for Windows Server Active Directory, modify the Mode setting.
Answer: A,D,E
Explanation:
Azure AD password protection is a feature that enhances password policies in an organization. On-premises deployment of password protection uses both the global and custom banned-password lists that are stored in Azure AD. It does the same checks on-premises as Azure AD does for cloud-based changes. These checks are performed during password changes and password reset scenarios.
You need to install the Azure AD Password Protection Proxy on a domain controller and install the Azure AD Password Protection DC Agent on all domain controllers. When the proxy and agent are installed and configured, Azure AD password protection will work.
In the exhibit, the password protection is configured in Audit mode. This is used for testing. To enforce the configured policy, you need to set the password protection setting to Enforced.
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/authentication/howto-password-ban-bad-on-premises- deploy
https://docs.microsoft.com/en-us/azure/active-directory/authentication/concept-password-ban-bad-on-premises
NEW QUESTION # 118
Which role should you assign to User1?
- A. Hygiene Management
- B. Records Management
- C. Security Administrator
- D. Security Reader
Answer: D
Explanation:
Explanation
* A user named User1 must be able to view all DLP reports from the Microsoft 365 admin center.
Users with the Security Reader role have global read-only access on security-related features, including all information in Microsoft 365 security center, Azure Active Directory, Identity Protection, Privileged Identity Management, as well as the ability to read Azure Active Directory sign-in reports and audit logs, and in Office
365 Security & Compliance Center.
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/users-groups-roles/directory-assign-admin-roles
Topic 2, Contoso, Ltd
This is a case study. Case studies are not timed separately. You can use as much exam time as you would like to complete each case. However, there may be additional case studies and sections on this exam. You must manage your time to ensure that you are able to complete all questions included on this exam in the time provided.
To answer the questions included in a case study, you will need to reference information that is provided in the case study. Case studies might contain exhibits and other resources that provide more information about the scenario that is described in the case study. Each question is independent of the other questions in this case study.
At the end of this case study, a review screen will appear. This screen allows you to review your answer and to make changes before you move to the next section of the exam. After you begin a new section, you cannot return to this section.
To start the case study
To display the first question in this case study, click the button. Use the buttons in the left pane to explore the content of the case study before you answer the questions. Clicking these buttons displays information such as business requirements, existing environment, and problem statements. When you are ready to answer a question, click the Overview Contoso, Ltd. is a consulting company that has a main office in Montreal and two branch offices in Seattle and New York.
The offices have the users and devices shown in the following table.
Contoso recently purchased a Microsoft 365 E5 subscription.
Existing Environment
The network contains an Active directory forest named contoso.com and a Microsoft Azure Active Directory (Azure AD) tenant named contoso.onmicrosoft.com.
You recently configured the forest to sync to the Azure AD tenant.
You add and then verify adatum.com as an additional domain name.
All servers run Windows Server 2016.
All desktop computers and laptops run Windows 10 Enterprise and are joined to contoso.com.
All the mobile devices in the Montreal and Seattle offices run Android. All the mobile devices in the New York office run iOS.
Contoso has the users shown in the following table.
Contoso has the groups shown in the following table.
Microsoft Office 365 licenses are assigned only to Group2.
The network also contains external users from a vendor company who have Microsoft accounts that use a suffix of @outlook.com.
Requirements
Planned Changes
Contoso plans to provide email addresses for all the users in the following domains:
* East.adatum.com
* Contoso.adatum.com
* Humongousinsurance.com
Technical Requirements
Contoso identifies the following technical requirements:
* All new users must be assigned Office 365 licenses automatically.
* The principle of least privilege must be used whenever possible.
Security Requirements
Contoso identifies the following security requirements:
* Vendors must be able to authenticate by using their Microsoft account when accessing Contoso resources.
* User2 must be able to view reports and schedule the email delivery of security and compliance reports.
* The members of Group1 must be required to answer a security question before changing their password.
* User3 must be able to manage Office 365 connectors.
* User4 must be able to reset User3 password.
NEW QUESTION # 119
Your company has 10,000 users who access all applications from an on-premises data center.
You plan to create a Microsoft 365 subscription and to migrate data to the cloud.
You plan to implement directory synchronization.
User account and group accounts must sync to Microsoft Azure Directory (Azure AD) successfully.
You discover that several user accounts fail to sync to Azure AD.
You need to identify which user accounts failed to sync. You must resolve the issue as quickly as possible.
What should you do?
- A. Run idfix.exe, and then click
- B. From Windows PowerShell, run the Start-AdSyncSyncCycle -PolicyType Delta command.
- C. Run idfix.exe, and then click
- D. From Active Directory Administrative Center, search for all the users, and then modify the properties of the user accounts.
Answer: C
NEW QUESTION # 120
......
To prepare for the Microsoft MS-100 exam, candidates can take advantage of various resources such as Microsoft official training courses, study guides, and practice tests. Candidates can also participate in online forums and communities to interact with other professionals and learn from their experiences.
Exam Valid Dumps with Instant Download Free Updates: https://www.dumpsquestion.com/MS-100-exam-dumps-collection.html
MS-100 Dumps First Attempt Guaranteed Success: https://drive.google.com/open?id=1lRB1yXyFVNQavEwbHcXGgDEL-H-sV_Ex