

Pass Your Exam With 100% Verified GCCC Exam Questions
GCCC Dumps PDF - GCCC Real Exam Questions Answers
NEW QUESTION 19
An analyst investigated unused organizational accounts. The investigation found that:
-10% of accounts still have their initial login password, indicating they were never used
-10% of accounts have not been used in over six months
Which change in policy would mitigate the security risk associated with both findings?
- A. Accounts without login activity for 15 days are automatically locked
- B. Accounts must have passwords of at least 8 characters, with one number or symbol
- C. Users are required to change their password at the next login after three months
Answer: A
NEW QUESTION 20
How does an organization's hardware inventory support the control for secure configurations?
- A. It provides a list of managed devices that should be secured
- B. It provides a list of unauthorized devices on the network
- C. It provides the MAC addresses for insecure network adapters
- D. It identifies the life cycle of manufacturer support for hardware devices
Answer: A
NEW QUESTION 21
The settings in the screenshot would be configured as part of which CIS Control?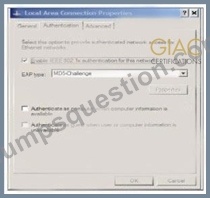
- A. Inventory and Control of Hardware Assets
- B. Account Monitoring and Control
- C. Application Software Security
- D. Controlled Use of Administrative Privileges
Answer: A
NEW QUESTION 22
Which of the following is a requirement in order to implement the principle of least privilege?
- A. Data normalization
- B. Discretionary Access Control (DAC)
- C. Mandatory Access Control (MAC)
- D. Data classification
Answer: D
NEW QUESTION 23
Which CIS Control includes storing system images on a hardened server, scanning production systems for out-of-date software, and using file integrity assessment tools like tripwire?
- A. Secure Configurations for Hardware and Software on Mobile Devices, Laptops, Workstations, and Servers
- B. Continuous Vulnerability Management
- C. Secure Configurations for Network Devices such as Firewalls, Routers and Switches
- D. Inventory of Authorized and Unauthorized Software
Answer: A
NEW QUESTION 24
Which approach is recommended by the CIS Controls for performing penetration tests?
- A. Complete intrusive tests on test systems
- B. Utilize a single attack vector at a time
- C. Document a single vulnerability per system
- D. Execute all tests during network maintenance windows
Answer: A
NEW QUESTION 25
Which projects enumerates or maps security issues to CVE?
- A. ISO 2700
- B. SCAP
- C. NIST
- D. CIS Controls
Answer: B
NEW QUESTION 26
An administrator looking at a web application's log file found login attempts by the same host over several seconds. Each user ID was attempted with three different passwords. The event took place over 5 seconds.
* ROOT
* TEST
* ADMIN
* SQL
* USER
* NAGIOSGUEST
What is the most likely source of this event?
- A. An automated tool that attempts to use a dictionary attack to infiltrate a website
- B. An attempt to use SQL Injection to gain information from a web-connected database
- C. An attempted Denial of Service attack by locking out administrative accounts
- D. An IT administrator attempting to use outdated credentials to enter the site
Answer: A
NEW QUESTION 27
Which of the following will decrease the likelihood of eavesdropping on a wireless network?
- A. Using EAP/TLS authentication and WPA2 with AES encryption
- B. Putting the wireless network on a separate VLAN
- C. Broadcasting in the 5Ghz frequency
- D. Using Wired Equivalent Protocol (WEP)
Answer: A
NEW QUESTION 28
During a security audit which test should result in a source packet failing to reach its intended destination?
- A. A packet originating from the company's DMZ is sent to a host on the company's internal network
- B. A new connection request from the internet is sent to the company's DNS server
- C. A packet originating from the company's internal network is sent to the company's DNS server
- D. A new connection request from the Internet is sent to a host on the company 's internal net work
Answer: D
NEW QUESTION 29
According to attack lifecycle models, what is the attacker's first step in compromising an organization?
- A. Reconnaissance
- B. Privilege Escalation
- C. Initial Compromise
- D. Exploitation
Answer: A
NEW QUESTION 30
An organization has installed a firewall for Boundary Defense. It allows only outbound traffic from internal workstations for web and SSH, allows connections from the internet to the DMZ, and allows guest wireless access to the internet only. How can an auditor validate these rules?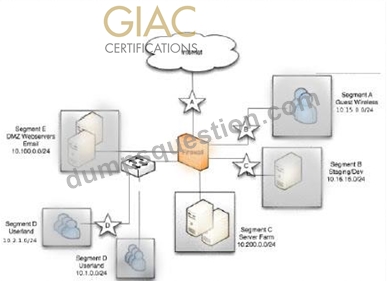
- A. Try to send email from a wireless guest account
- B. Try to access the internal network from the wireless router
- C. Check for packets going from the Internet to the Web server
- D. Check for packages going from the web server to the user workstations
Answer: B
NEW QUESTION 31
What is the list displaying?
- A. Allowed program in a software inventory application
- B. Installed software on an end-user device
- C. Missing patches from a patching server
- D. Unauthorized programs detected in a software inventory
Answer: A
NEW QUESTION 32
An attacker is able to successfully access a web application as root using ' or 1 = 1 . as the password. The successful access indicates a failure of what process?
- A. Input Validation
- B. URL Encoding
- C. Account Management
- D. Output Sanitization
Answer: A
NEW QUESTION 33
How often should the security awareness program be communicated to employees?
- A. Monthly
- B. At orientation and review times
- C. Continuously
- D. Annually
Answer: C
NEW QUESTION 34
A global corporation has major data centers in Seattle, New York, London and Tokyo. Which of the following is the correct approach from an intrusion detection and event correlation perspective?
- A. Configure all data center systems to use local time
- B. Synchronize between Seattle and New York, and use local time for London and Tokyo
- C. Configure all systems to use their default time settings
- D. Configure all data center systems to use GMT time
Answer: A
NEW QUESTION 35
When evaluating the Wireless Access Control CIS Control, which of the following systems needs to be tested?
- A. 802.1x authentication systems
- B. Log management system
- C. Data classification and access baselines
- D. PII data scanner
Answer: A
NEW QUESTION 36
An organization has implemented a policy to continually detect and remove malware from its network. Which of the following is a detective control needed for this?
- A. Network Intrusion Prevention sends alerts when RST packets are received
- B. Network Intrusion Detection devices sends alerts when signatures are updated
- C. Host-based firewall sends alerts when packets are sent to a closed port
- D. Host-based anti-virus sends alerts to a central security console
Answer: D
NEW QUESTION 37
......
GIAC GCCC Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
| Topic 6 |
|
| Topic 7 |
|
| Topic 8 |
|
| Topic 9 |
|
| Topic 10 |
|
| Topic 11 |
|
GCCC Dumps 100 Pass Guarantee With Latest Demo: https://www.dumpsquestion.com/GCCC-exam-dumps-collection.html
Prepare GCCC Question Answers Free Update With 100% Exam Passing Guarantee [2021]: https://drive.google.com/open?id=1zhLAkVzHk4UF2sss609scId20s9FJPZ0