

SC-200 Certification Exam Dumps Questions in here [Dec-2021]
Updated SC-200 Exam Practice Test Questions
NEW QUESTION 18
The issue for which team can be resolved by using Microsoft Defender for Endpoint?
- A. marketing
- B. executive
- C. sales
Answer: C
Explanation:
Reference:
https://docs.microsoft.com/en-us/windows/security/threat-protection/microsoft-defender-atp/microsoft-defender-atp-ios
NEW QUESTION 19
Your company uses Azure Security Center and Azure Defender.
The security operations team at the company informs you that it does NOT receive email notifications for security alerts.
What should you configure in Security Center to enable the email notifications?
- A. Pricing & settings
- B. Security solutions
- C. Security alerts
- D. Azure Defender
- E. Security policy
Answer: A
Explanation:
Section: [none]
Explanation/Reference:
https://docs.microsoft.com/en-us/azure/security-center/security-center-provide-security-contact-details
NEW QUESTION 20
You have resources in Azure and Google cloud.
You need to ingest Google Cloud Platform (GCP) data into Azure Defender.
In which order should you perform the actions? To answer, move all actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation:
Explanation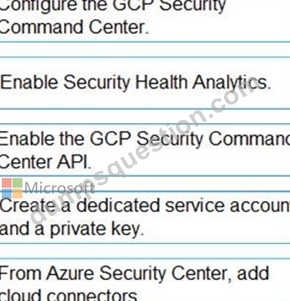
Reference:
https://docs.microsoft.com/en-us/azure/security-center/quickstart-onboard-gcp
NEW QUESTION 21
You have the following advanced hunting query in Microsoft 365 Defender.
You need to receive an alert when any process disables System Restore on a device managed by Microsoft Defender during the last 24 hours.
Which two actions should you perform? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
- A. Add DeviceId and ReportId to the output of the query.
- B. Create a suppression rule.
- C. Add | order by Timestamp to the query.
- D. Create a detection rule.
- E. Replace DeviceProcessEvents with DeviceNetworkEvents.
Answer: A,D
Explanation:
Reference:
https://docs.microsoft.com/en-us/windows/security/threat-protection/microsoft-defender-atp/custom-detection- rules
NEW QUESTION 22
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You use Azure Security Center.
You receive a security alert in Security Center.
You need to view recommendations to resolve the alert in Security Center.
Solution: From Security alerts, you select the alert, select Take Action, and then expand the Mitigate the threat section.
Does this meet the goal?
- A. No
- B. Yes
Answer: B
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/security-center/security-center-managing-and-responding-alerts
NEW QUESTION 23
DRAG DROP
You plan to connect an external solution that will send Common Event Format (CEF) messages to Azure Sentinel.
You need to deploy the log forwarder.
Which three actions should you perform in sequence? To answer, move the appropriate actions form the list of actions to the answer area and arrange them in the correct order.
Select and Place:
Answer:
Explanation:
Section: [none]
Explanation/Reference:
https://docs.microsoft.com/en-us/azure/sentinel/connect-cef-agent?tabs=rsyslog
NEW QUESTION 24
Your company stores the data for every project in a different Azure subscription. All the subscriptions use the same Azure Active Directory (Azure AD) tenant.
Every project consists of multiple Azure virtual machines that run Windows Server. The Windows events of the virtual machines are stored in a Log Analytics workspace in each machine's respective subscription.
You deploy Azure Sentinel to a new Azure subscription.
You need to perform hunting queries in Azure Sentinel to search across all the Log Analytics workspaces of all the subscriptions.
Which two actions should you perform? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
- A. Add the Azure Sentinel solution to each workspace.
- B. Create a query that uses the workspaceexpression and the unionoperator.
- C. Add the Security Events connector to the Azure Sentinel workspace.
- D. Use the aliasstatement.
- E. Create a query that uses the resourceexpression and the aliasoperator.
Answer: A,B
Explanation:
Section: [none]
Explanation/Reference:
https://docs.microsoft.com/en-us/azure/sentinel/extend-sentinel-across-workspaces-tenants
NEW QUESTION 25
You are configuring Azure Sentinel.
You need to send a Microsoft Teams message to a channel whenever a sign-in from a suspicious IP address is detected.
Which two actions should you perform in Azure Sentinel? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
- A. Associate a playbook to an incident.
- B. Enable Entity behavior analytics.
- C. Add a playbook.
- D. Enable the Fusion rule.
- E. Create a workbook.
Answer: A,C
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/sentinel/tutorial-respond-threats-playbook
NEW QUESTION 26
From Azure Sentinel, you open the Investigation pane for a high-severity incident as shown in the following exhibit.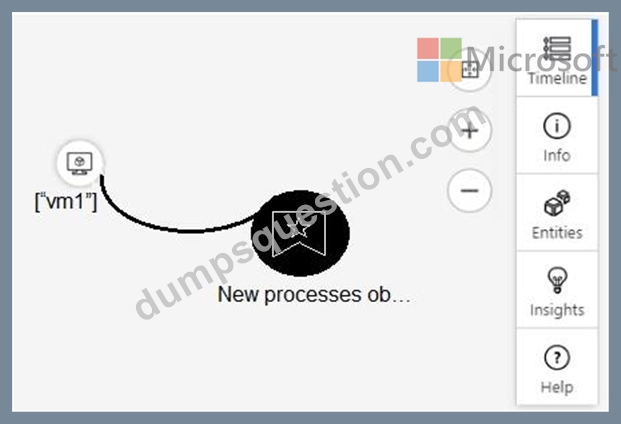
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.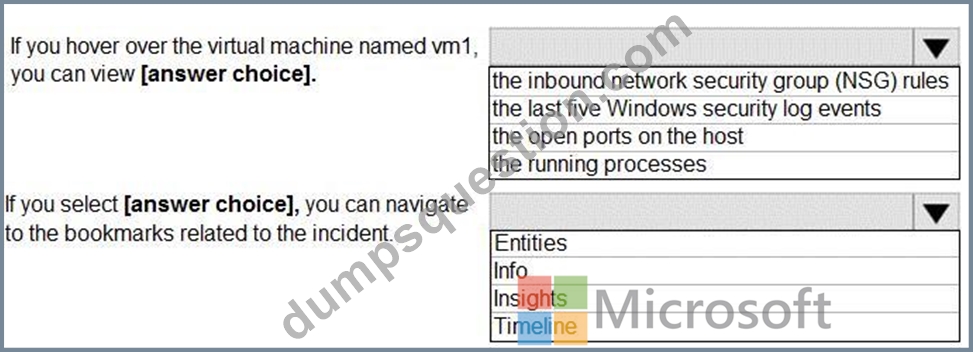
Answer:
Explanation:
Explanation
Reference:
https://docs.microsoft.com/en-us/azure/sentinel/tutorial-investigate-cases#use-the-investigation-graph-to-deep-di
NEW QUESTION 27
You need to use an Azure Resource Manager template to create a workflow automation that will trigger an automatic remediation when specific security alerts are received by Azure Security Center.
How should you complete the portion of the template that will provision the required Azure resources? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.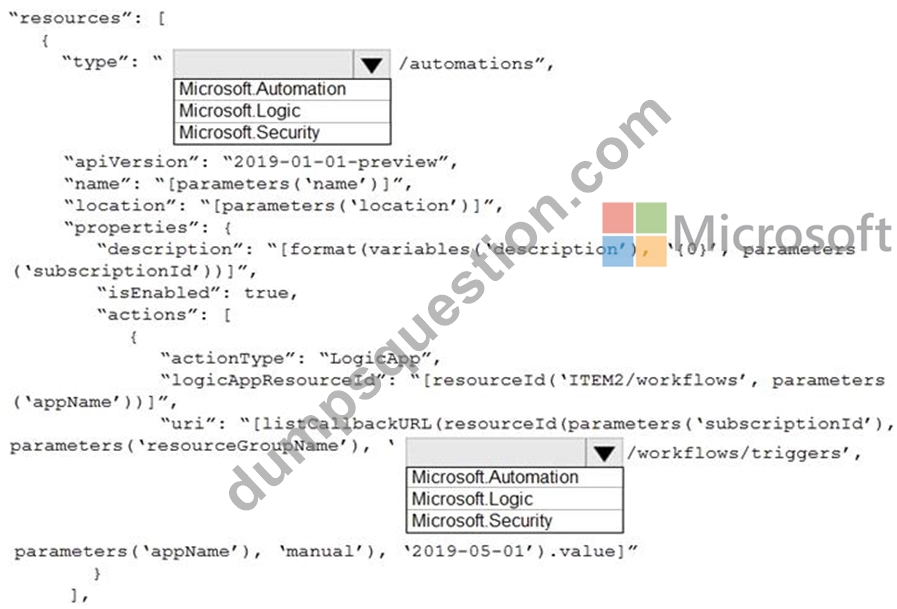
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/security-center/quickstart-automation-alert
NEW QUESTION 28
You plan to create a custom Azure Sentinel query that will provide a visual representation of the security alerts generated by Azure Security Center.
You need to create a query that will be used to display a bar graph. What should you include in the query?
- A. extend
- B. bin
- C. workspace
- D. count
Answer: D
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/azure-monitor/visualize/workbooks-chart-visualizations
NEW QUESTION 29
You create an Azure subscription.
You enable Azure Defender for the subscription.
You need to use Azure Defender to protect on-premises computers.
What should you do on the on-premises computers?
- A. Install the Connected Machine agent.
- B. Install the Dependency agent.
- C. Install the Log Analytics agent.
- D. Configure the Hybrid Runbook Worker role.
Answer: C
Explanation:
Security Center collects data from your Azure virtual machines (VMs), virtual machine scale sets, IaaS containers, and non-Azure (including on-premises) machines to monitor for security vulnerabilities and threats.
Data is collected using:
The Log Analytics agent, which reads various security-related configurations and event logs from the machine and copies the data to your workspace for analysis. Examples of such data are: operating system type and version, operating system logs (Windows event logs), running processes, machine name, IP addresses, and logged in user.
Security extensions, such as the Azure Policy Add-on for Kubernetes, which can also provide data to Security Center regarding specialized resource types.
Reference:
https://docs.microsoft.com/en-us/azure/security-center/security-center-enable-data-collection
NEW QUESTION 30
You need to restrict cloud apps running on CLIENT1 to meet the Microsoft Defender for Endpoint requirements.
Which two configurations should you modify? Each correct answer present part of the solution.
NOTE: Each correct selection is worth one point.
- A. Advanced features from Settings in Microsoft Defender Security Center
- B. Cloud App Security anomaly detection policies
- C. the Onboarding settings from Device management in Microsoft Defender Security Center
- D. the Cloud Discovery settings in Cloud App Security
Answer: A,D
Explanation:
All Cloud App Security unsanctioned apps must be blocked on the Windows 10 computers by using Microsoft Defender for Endpoint.
Reference:
https://docs.microsoft.com/en-us/cloud-app-security/mde-govern
NEW QUESTION 31
Your company uses Azure Sentinel.
A new security analyst reports that she cannot assign and resolve incidents in Azure Sentinel.
You need to ensure that the analyst can assign and resolve incidents. The solution must use the principle of least privilege.
Which role should you assign to the analyst?
- A. Azure Sentinel Contributor
- B. Logic App Contributor
- C. Azure Sentinel Responder
- D. Azure Sentinel Reader
Answer: C
Explanation:
Section: [none]
Explanation/Reference:
https://docs.microsoft.com/en-us/azure/sentinel/roles
NEW QUESTION 32
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You are configuring Azure Sentinel.
You need to create an incident in Azure Sentinel when a sign-in to an Azure virtual machine from a malicious IP address is detected.
Solution: You create a scheduled query rule for a data connector.
Does this meet the goal?
- A. No
- B. Yes
Answer: A
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/sentinel/connect-azure-security-center
NEW QUESTION 33
You are configuring Microsoft Cloud App Security.
You have a custom threat detection policy based on the IP address ranges of your company's United States-based offices.
You receive many alerts related to impossible travel and sign-ins from risky IP addresses.
You determine that 99% of the alerts are legitimate sign-ins from your corporate offices.
You need to prevent alerts for legitimate sign-ins from known locations.
Which two actions should you perform? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
- A. Add the IP addresses to the corporate address range category.
- B. Increase the sensitivity level of the impossible travel anomaly detection policy.
- C. Override automatic data enrichment.
- D. Create an activity policy that has an exclusion for the IP addresses.
- E. Add the IP addresses to the other address range category and add a tag.
Answer: C,E
NEW QUESTION 34
You need to remediate active attacks to meet the technical requirements.
What should you include in the solution?
- A. Azure Automation runbooks
- B. Azure Logic Apps
- C. Azure Functions
D Azure Sentinel livestreams
Answer: B
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/sentinel/automate-responses-with-playbooks
NEW QUESTION 35
You manage the security posture of an Azure subscription that contains two virtual machines name vm1 and vm2.
The secure score in Azure Security Center is shown in the Security Center exhibit. (Click the Security Center tab.)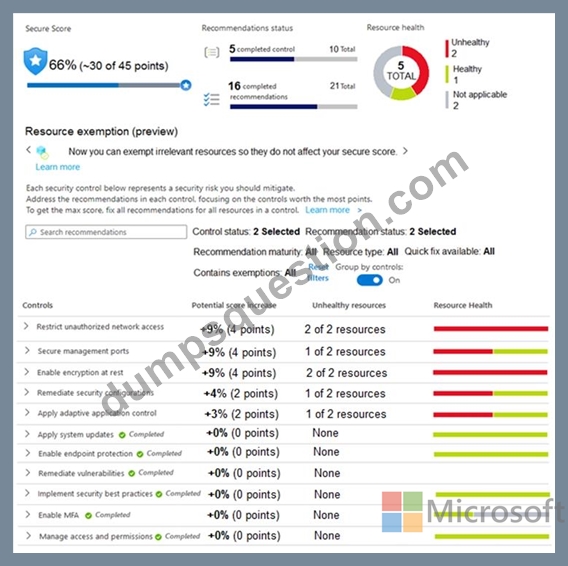
Azure Policy assignments are configured as shown in the Policies exhibit. (Click the Policies tab.)
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
Reference:
https://techcommunity.microsoft.com/t5/azure-security-center/security-control-restrict-unauthorized-network-acc
https://techcommunity.microsoft.com/t5/azure-security-center/security-control-secure-management-ports/ba-p/15
NEW QUESTION 36
You need to configure DC1 to meet the business requirements.
Which four actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation:
Explanation
Text Description automatically generated with medium confidence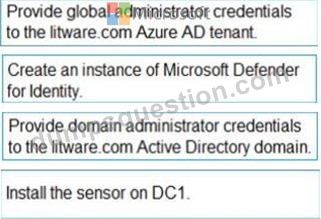
Step 1: log in to https://portal.atp.azure.com as a global admin
Step 2: Create the instance
Step 3. Connect the instance to Active Directory
Step 4. Download and install the sensor.
Reference:
https://docs.microsoft.com/en-us/defender-for-identity/install-step1
https://docs.microsoft.com/en-us/defender-for-identity/install-step4
NEW QUESTION 37
You need to recommend a solution to meet the technical requirements for the Azure virtual machines. What should you include in the recommendation?
- A. just-in-time (JIT) access
- B. Azure Application Gateway
- C. Azure Defender
- D. Azure Firewall
Answer: C
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/security-center/azure-defender
NEW QUESTION 38
You have an Azure subscription.
You need to delegate permissions to meet the following requirements:
Enable and disable Azure Defender.
Apply security recommendations to resource.
The solution must use the principle of least privilege.
Which Azure Security Center role should you use for each requirement? To answer, drag the appropriate roles to the correct requirements. Each role may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
Answer:
Explanation: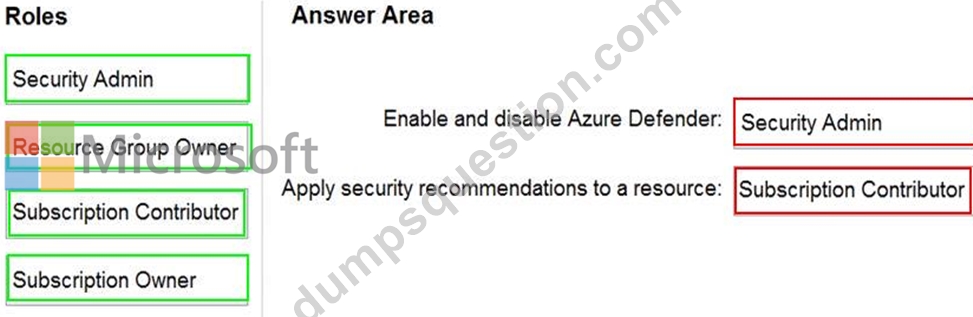
Reference:
https://docs.microsoft.com/en-us/azure/security-center/security-center-permissions
NEW QUESTION 39
......
Skills measured
- Mitigate threats using Microsoft 365 Defender (25-30%)
- The content of this exam was updated on July 23, 2021. Please download the exam skills outline below to see what changed.
- Mitigate threats using Azure Defender (25-30%)
- Mitigate threats using Azure Sentinel (40-45%)
Verified SC-200 dumps Q&As 100% Pass in First Attempt Guaranteed Updated Dump: https://drive.google.com/open?id=1c3BUe6HseWdMYRQRc38eNLYdFnTfwDGs
Pass Microsoft Certified: Security Operations Analyst Associate SC-200 Exam With 100 Questions: https://www.dumpsquestion.com/SC-200-exam-dumps-collection.html