

View SC-100 Exam Question Dumps With Latest Demo [May 30, 2026]
Free SC-100 Test Questions Real Practice Test Questions
The Microsoft Cybersecurity Architect certification exam is divided into four main sections, each of which covers a different aspect of cybersecurity architecture. The first section focuses on the identification of security threats and vulnerabilities, the second section covers the design and implementation of security solutions, the third section focuses on risk management, and the fourth section covers the management of compliance and regulations. Each section of the exam is designed to test the candidate's knowledge and skills in specific areas of cybersecurity architecture.
NEW QUESTION # 116
You have a Microsoft 365 subscription that is protected by using Microsoft 365 Defender You are designing a security operations strategy that will use Microsoft Sentinel to monitor events from Microsoft 365 and Microsoft 365 Defender You need to recommend a solution to meet the following requirements:
* Integrate Microsoft Sentinel with a third-party security vendor to access information about known malware
* Automatically generate incidents when the IP address of a command-and control server is detected in the events What should you configure in Microsoft Sentinel to meet each requirement? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.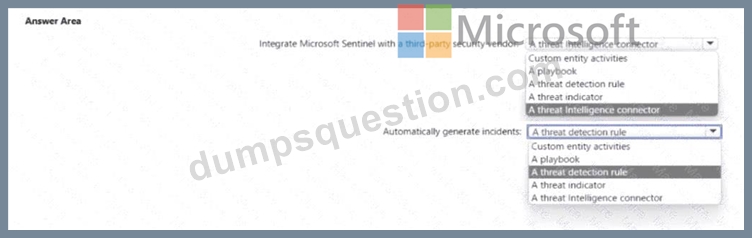
Answer:
Explanation: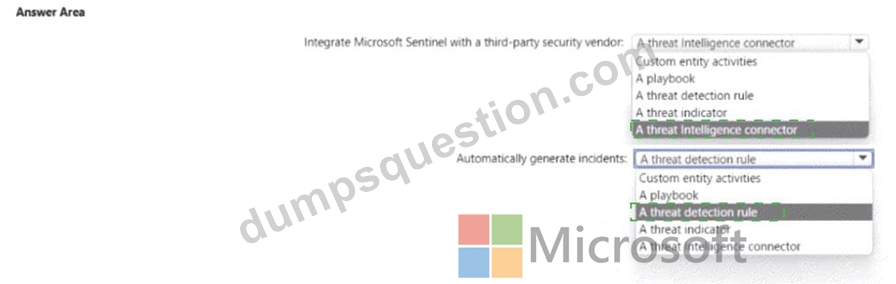
Explanation: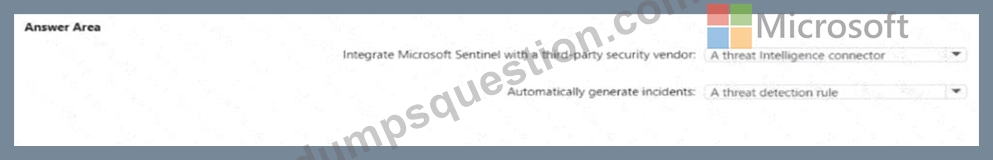
NEW QUESTION # 117
You have an Azure subscription. The subscription contains 200 virtual machines that run Windows Server 2022 and are protected by using Microsoft Defender for Servers Plan 1. You have an Amazon Web Services (AWS) subscription.
To the AWS subscription, you plan to deploy 100 virtual machines that run Windows Server 2022.
You need to recommend which agent to deploy to the virtual machines in the AWS subscription.
The solution must meet the following requirements:
- Provide consistent workload protection across all cloud platforms.
- Minimize the number of agents deployed to each virtual machine.
What should you recommend?
- A. the Azure Monitor Agent
- B. the log Analytics agent
- C. the Azure Connected Machine agent
- D. the Microsoft Defender for Endpoint agent
Answer: C
Explanation:
The Azure Connected Machine agent can be used to manage Windows Server 2022 virtual machines hosted on Amazon Web Services (AWS). This allows you to extend Azure management capabilities to your non-Azure VMs, including those running on AWS.
Reference:
https://learn.microsoft.com/en-us/azure/azure-arc/servers/agent-overview
NEW QUESTION # 118
You use Azure Pipelines with Azure Repos to implement continuous integration and continuous deployment (O/CD) workflows for the deployment of applications to Azure. You need to recommend what to include in dynamic application security testing (DAST) based on the principles of the Microsoft Cloud Adoption Framework for Azure. What should you recommend?
- A. threat modeling
- B. penetration testing
- C. dependency testing
- D. unit testing
Answer: C
NEW QUESTION # 119
You have a Microsoft 365 subscription and an Azure subscription. Microsoft 365 Defender and Microsoft Defender for Cloud are enabled.
The Azure subscription contains a Microsoft Sentinel workspace. Microsoft Sentinel data connectors are configured for Microsoft 365, Microsoft 365 Defender, Defender for Cloud, and Azure.
You plan to deploy Azure virtual machines that will run Windows Server.
You need to enable extended detection and response (EDR) and security orchestration, automation, and response (SOAR) capabilities for Microsoft Sentinel.
How should you recommend enabling each capability? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.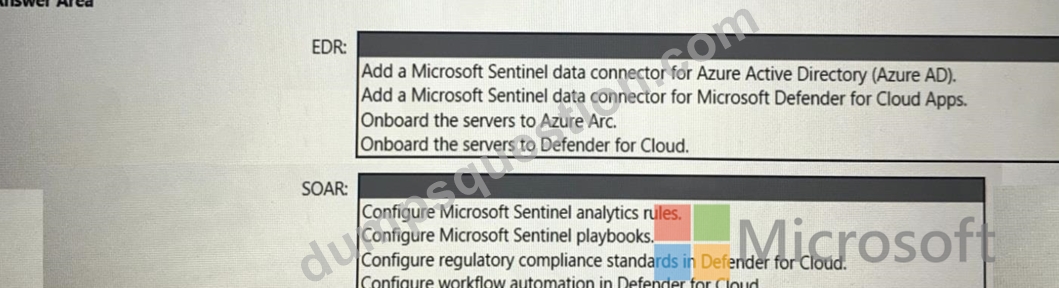
Answer:
Explanation: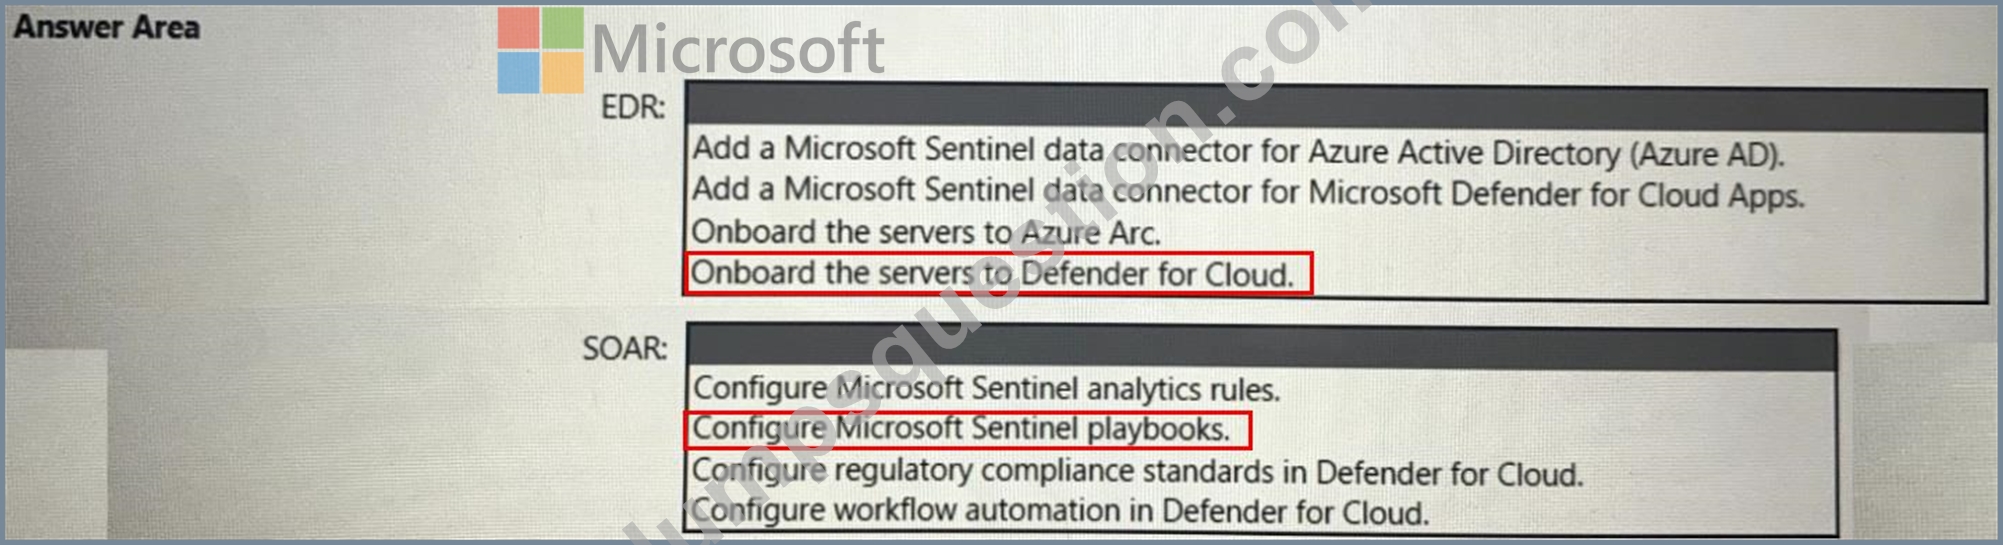
NEW QUESTION # 120
You have an Azure subscription.
You plan to deploy Azure App Services apps by using Azure DevOps.
You need to recommend a solution to ensure that deployed apps maintain compliance with Microsoft cloud security benchmark (MCSB) recommendations.
What should you include in the recommendation?
- A. Azure Policy
- B. Microsoft Defender for App Service
- C. DevOps security in Microsoft Defender for Cloud
- D. a branch policy in Azure DevOps
Answer: A
Explanation:
This security baseline applies guidance from the Microsoft cloud security benchmark version 1.0 to App Service. The Microsoft cloud security benchmark provides recommendations on how you can secure your cloud solutions on Azure. The content is grouped by the security controls defined by the Microsoft cloud security benchmark and the related guidance applicable to App Service.
You can monitor this security baseline and its recommendations using Microsoft Defender for Cloud. Azure Policy definitions will be listed in the Regulatory Compliance section of the Microsoft Defender for Cloud portal page.
When a feature has relevant Azure Policy Definitions, they are listed in this baseline to help you measure compliance with the Microsoft cloud security benchmark controls and recommendations.
Some recommendations may require a paid Microsoft Defender plan to enable certain security scenarios.
Reference:
https://learn.microsoft.com/en-us/security/benchmark/azure/baselines/app-service-security- baseline
NEW QUESTION # 121
You need to recommend a SIEM and SOAR strategy that meets the hybrid requirements, the Microsoft Sentinel requirements, and the regulatory compliance requirements.
What should you recommend? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.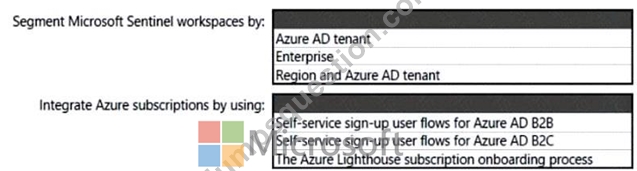
Answer:
Explanation: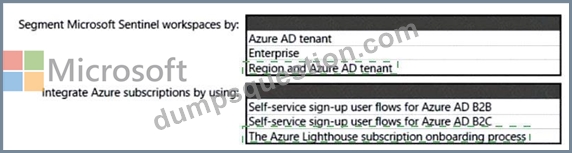
Explanation
Segment Microsoft Sentinel workspaces by: Region and Azure AD tenant
Lighthouse subscription
NEW QUESTION # 122
You are designing security for a runbook in an Azure Automation account. The runbook will copy data to Azure Data Lake Storage Gen2.
You need to recommend a solution to secure the components of the copy process.
What should you include in the recommendation for each component? To answer, select the appropriate options in the answer are a. NOTE: Each correct selection is worth one point.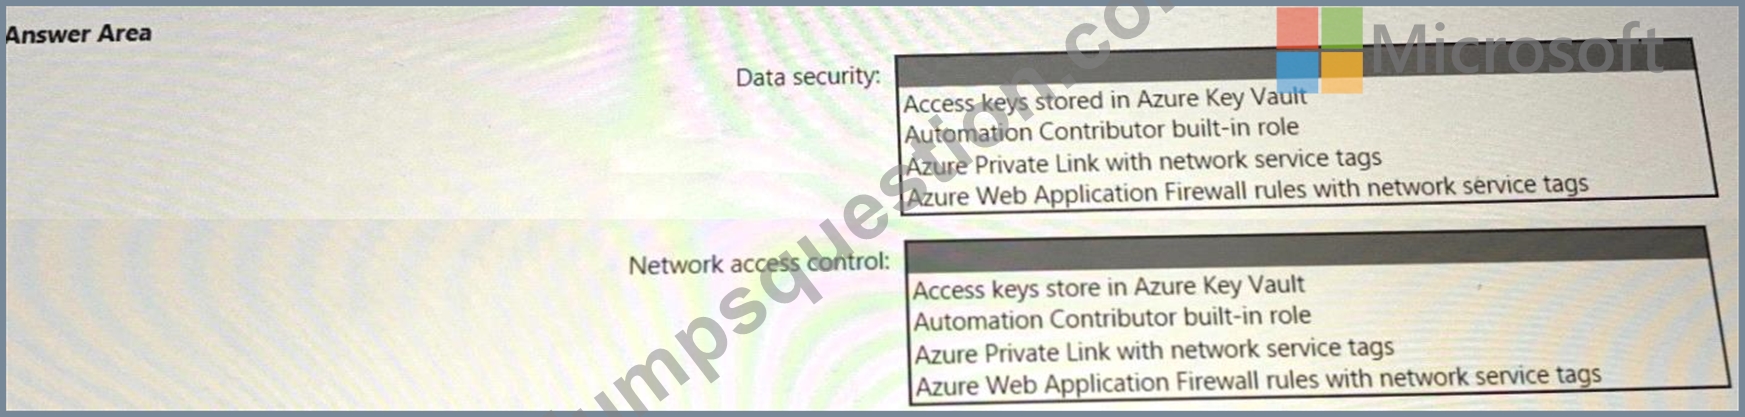
Answer:
Explanation: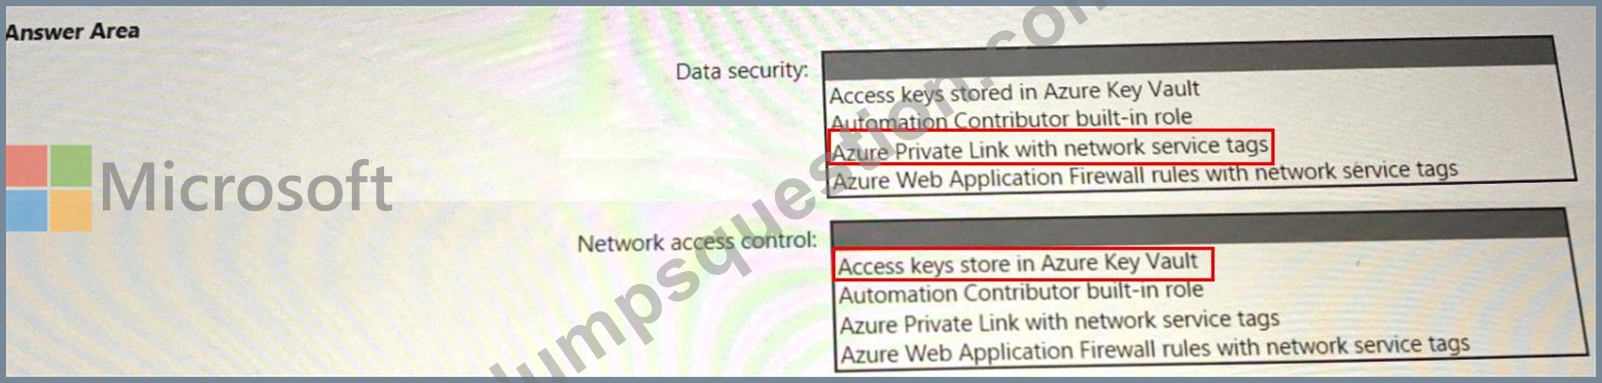
NEW QUESTION # 123
Your company is designing an application architecture for Azure App Service Environment (ASE) web apps as shown in the exhibit. (Click the Exhibit tab.)
Communication between the on-premises network and Azure uses an ExpressRoute connection.
You need to recommend a solution to ensure that the web apps can communicate with the on-premises application server. The solution must minimize the number of public IP addresses that are allowed to access the on-premises network.
What should you include in the recommendation?
- A. Azure Firewall with policy rule sets
- B. Azure Application Gateway v2 with user-defined routes (UDRs).
- C. Azure Traffic Manager with priority traffic-routing methods
- D. Azure Front Door with Azure Web Application Firewall (WAF)
Answer: C
NEW QUESTION # 124
You are creating the security recommendations for an Azure App Service web app named App1.
App1 has the following specifications:
* Users will request access to App1 through the My Apps portal. A human resources manager will approve the requests.
* Users will authenticate by using Azure Active Directory (Azure AD) user accounts.
You need to recommend an access security architecture for App1.
What should you include in the recommendation? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.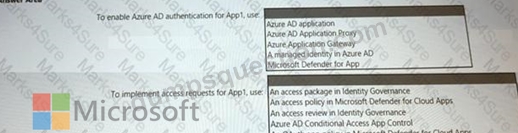
Answer:
Explanation: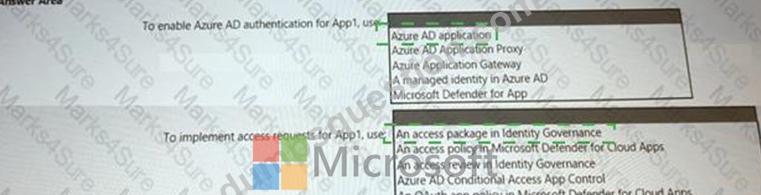
Explanation:
Box 1 is the Azure AD Application
https://docs.microsoft.com/en-us/azure/active-directory/develop/quickstart-register-app Box 2 is Access Package in Identity Governance
https://docs.microsoft.com/en-us/azure/active-directory/governance/entitlement-management-access-package-cre
NEW QUESTION # 125
You are designing an auditing solution for Azure landing zones that will contain the following components:
* SQL audit logs for Azure SQL databases
* Windows Security logs from Azure virtual machines
* Azure App Service audit logs from App Service web apps
You need to recommend a centralized logging solution for the landing zones. The solution must meet the following requirements:
* Log all privileged access.
* Retain logs for at least 365 days.
* Minimize costs.
What should you include in the recommendation? To answer, select the appropriate options in the answer are
a. NOTE: Each correct selection is worth one point.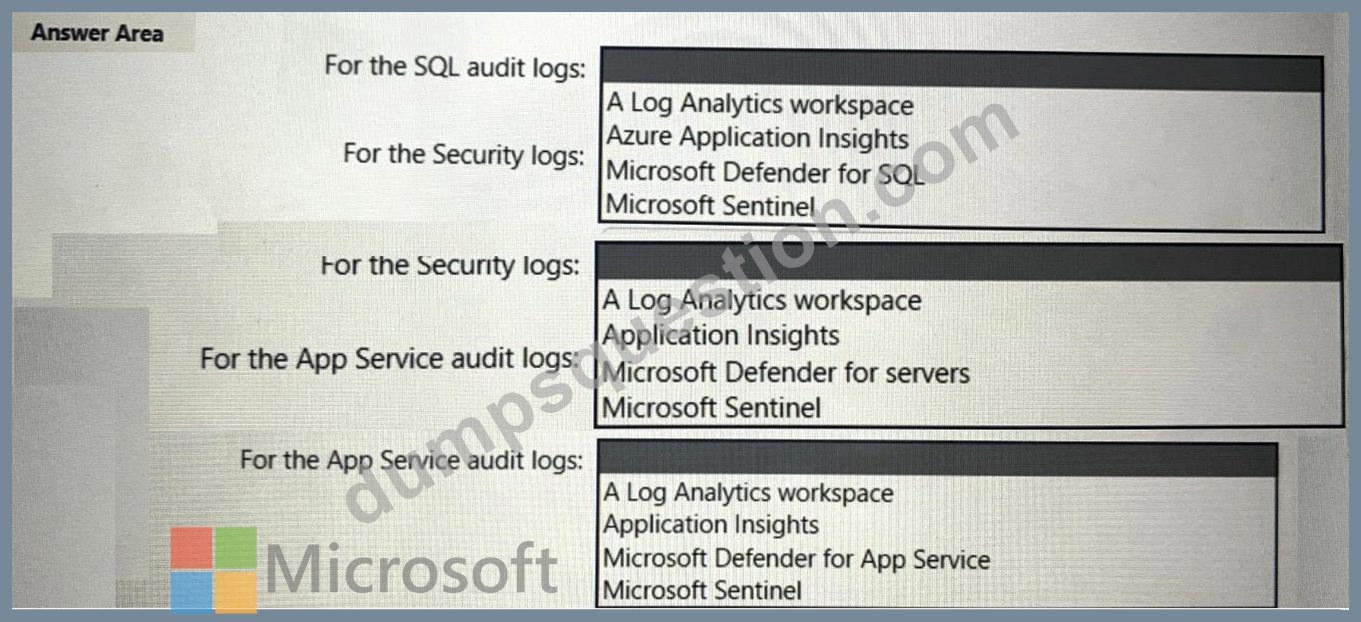
Answer:
Explanation: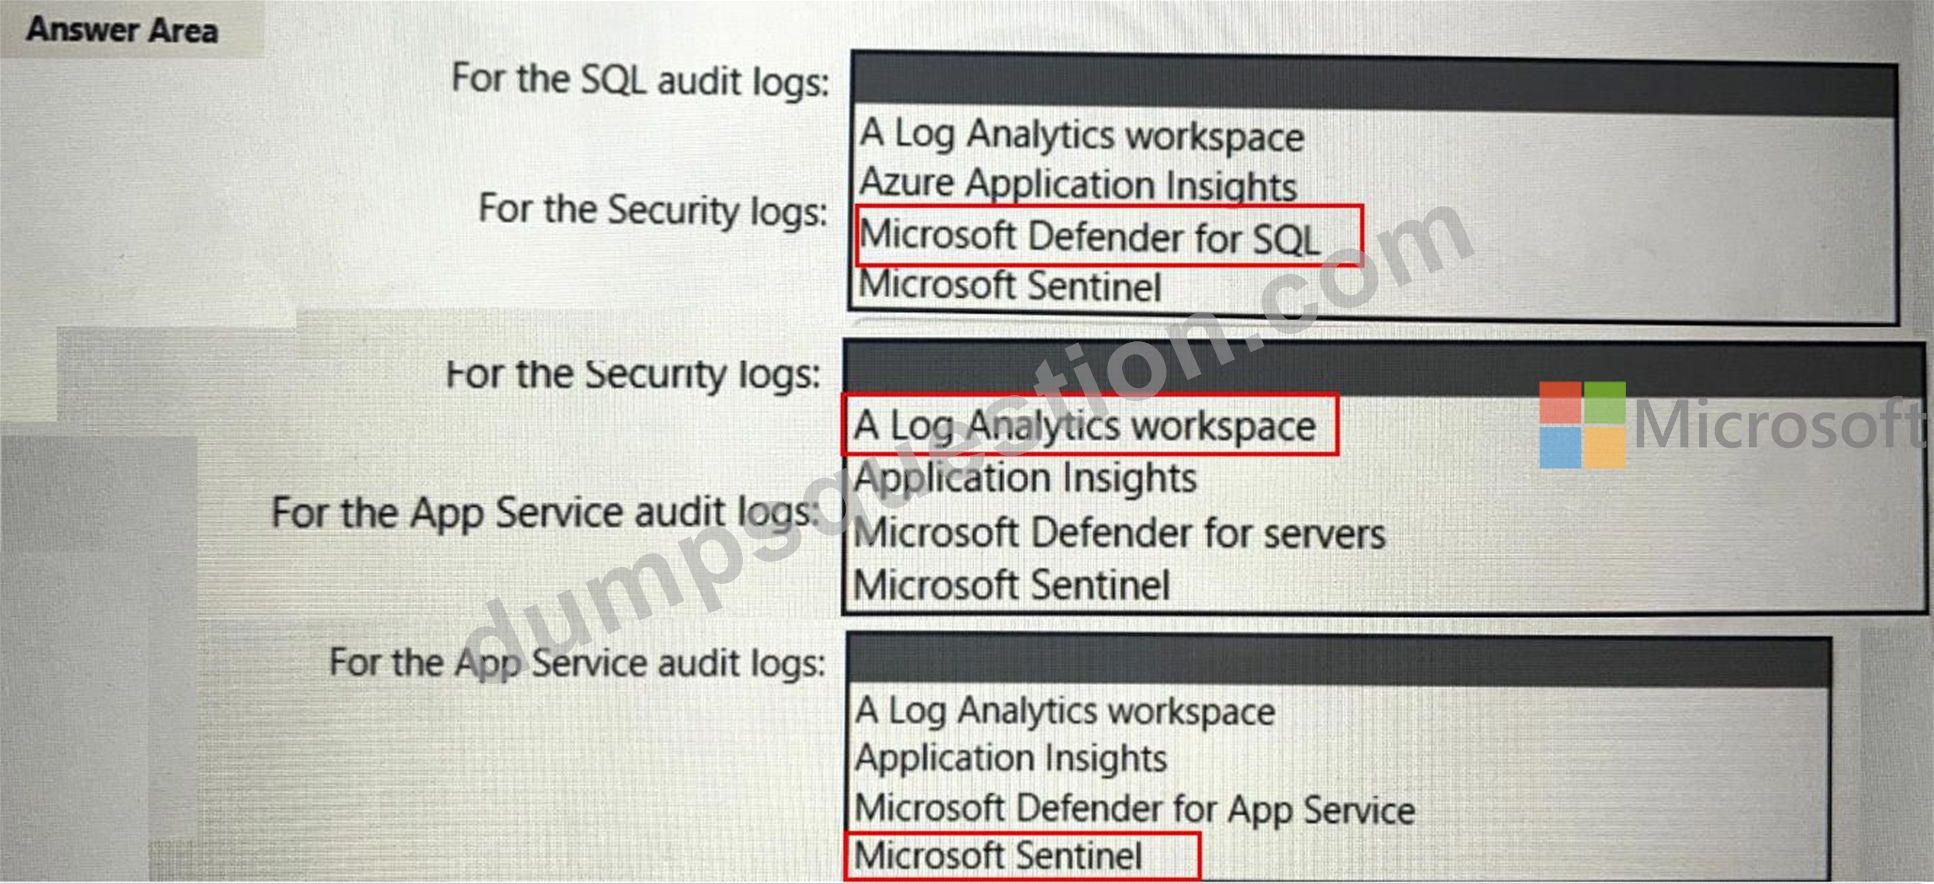
NEW QUESTION # 126
You need to recommend a strategy for securing the litware.com forest. The solution must meet the identity requirements. What should you include in the recommendation? To answer, select the appropriate options in the answer area. NOTE; Each correct selection is worth one point.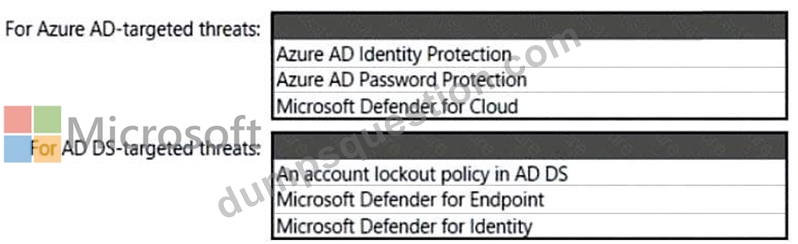
Answer:
Explanation: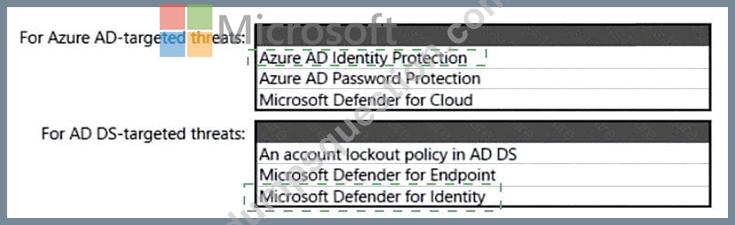
Explanation:
1. Azure AD Identity Protection
Brute Force Detection: https://docs.microsoft.com/en-us/azure/active-directory/identity-protection/overview- identity-protection
2. Defender for Identity
MDI can detect brute force attacks: ref: https://docs.microsoft.com/en-us/defender-for-identity/compromised- credentials-alerts#suspected-brute-force-attack-ldap-external-id-2004
NEW QUESTION # 127
Hotspot Question
Your client interacts with its customers using custom-built mobile apps. Current authentication and authorization information is stored in individually maintained Azure-based databases. The client has asked you to design a solution that allows authentication and authorization to be centralized. You recommend that your client deploy Azure AD and implement OAuth 2.0 for authorization.
You need to help your client identify the process that is performed by each OAuth 2.0 party.
Which process should you identify for each of the roles? To answer, select the appropriate options from the drop-down menus.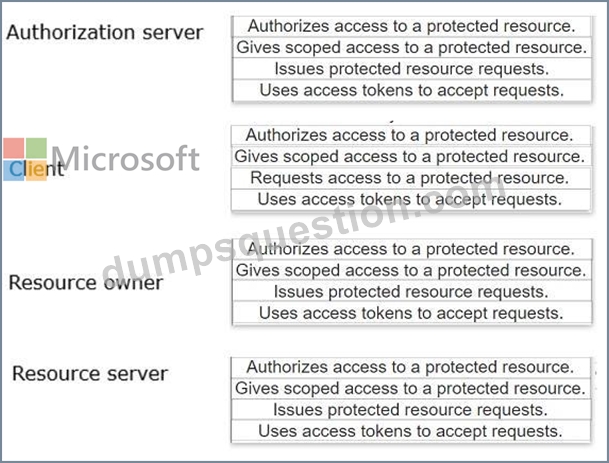
Answer:
Explanation: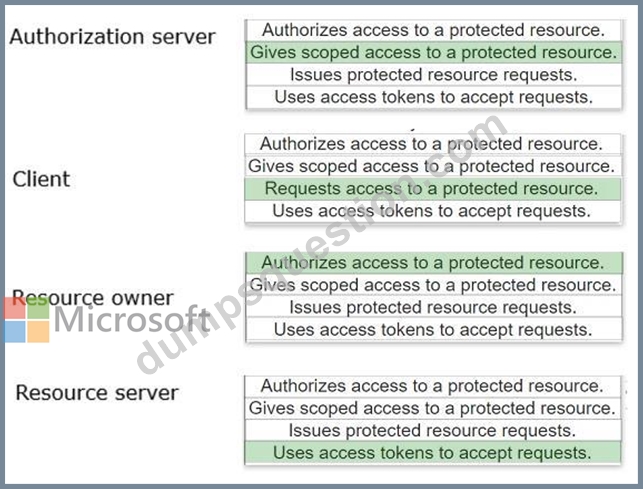
NEW QUESTION # 128
Your on-premises network contains an e-commerce web app that was developed in Angular and Nodejs. The web app uses a MongoDB database. You plan to migrate the web app to Azure. The solution architecture team proposes the following architecture as an Azure landing zone.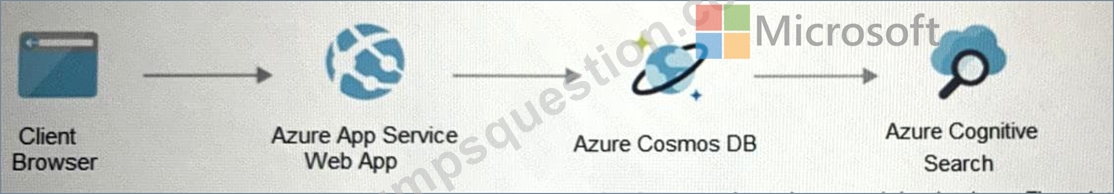
You need to provide recommendations to secure the connection between the web app and the database. The solution must follow the Zero Trust model.
Solution: You recommend creating private endpoints for the web app and the database layer.
Does this meet the goal?
- A. Yes
- B. No
Answer: A
Explanation:
Explanation
When using Azure-provided PaaS services (e.g., Azure Storage, Azure Cosmos DB, or Azure Web App, use the PrivateLink connectivity option to ensure all data exchanges are over the private IP space and the traffic never leaves the Microsoft network.
https://docs.microsoft.com/en-us/azure/cosmos-db/how-to-configure-private-endpoints
NEW QUESTION # 129
You have an Azure subscription that is used as an Azure landing zone for an application.
You need to evaluate the security posture of all the workloads in the landing zone.
What should you do first?
- A. Obtain Azure Active Directory Premium Plan 2 licenses.
- B. Enable the Defender plan for all resource types in Microsoft Defender for Cloud.
- C. Add Microsoft Sentinel data connectors.
- D. Configure Continuous Integration/Continuous Deployment (CI/CD) vulnerability scanning.
Answer: B
Explanation:
https://learn.microsoft.com/en-us/training/modules/evaluate-security-posture-recommend- technical-strategies-to-manage-risk/5-design-security-for-azure-landing-zone
NEW QUESTION # 130
You need to recommend a solution to resolve the virtual machine issue. What should you include in the recommendation?
- A. Onboard the virtual machines to Microsoft Defender for Endpoint.
- B. Onboard the virtual machines to Azure Arc.
- C. Enable the Qualys scanner in Defender for Cloud.
- D. Create a device compliance policy in Microsoft Endpoint Manager.
Answer: A
Explanation:
Topic 1, Fabrikam, Inc
On-premises Environment
The on-premises network contains a single Active Directory Domain Services (AD DS) domain named corp.fabrikam.com.
Azure Environment
Fabrikam has the following Azure resources:
* An Azure Active Directory (Azure AD) tenant named fabrikam.onmicrosoft.com that syncs with corp.fabnkam.com
* A single Azure subscription named Sub1
* A virtual network named Vnetl in the East US Azure region
* A virtual network named Vnet2 in the West Europe Azure region
* An instance of Azure Front Door named FD1 that has Azure Web Application Firewall (WAR enabled
* A Microsoft Sentinel workspace
* An Azure SQL database named ClaimsDB that contains a table named ClaimDetails
* 20 virtual machines that are configured as application servers and are NOT onboarded to Microsoft Defender for Cloud
* A resource group named TestRG that is used for testing purposes only
* An Azure Virtual Desktop host pool that contains personal assigned session hosts All the resources in Sub1 are in either the East US or the West Europe region.
Partners
Fabrikam has contracted a company named Contoso, Ltd. to develop applications. Contoso has the following infrastructure-.
* An Azure AD tenant named contoso.onmicrosoft.com
* An Amazon Web Services (AWS) implementation named ContosoAWS1 that contains AWS EC2 instances used to host test workloads for the applications of Fabrikam Developers at Contoso will connect to the resources of Fabrikam to test or update applications. The developers will be added to a security Group named Contoso Developers in fabrikam.onmicrosoft.com that will be assigned to roles in Sub1.
The ContosoDevelopers group is assigned the db.owner role for the ClaimsDB database.
Compliance Event
Fabrikam deploys the following compliance environment:
* Defender for Cloud is configured to assess all the resources in Sub1 for compliance to the HIPAA HITRUST standard.
* Currently, resources that are noncompliant with the HIPAA HITRUST standard are remediated manually.
* Qualys is used as the standard vulnerability assessment tool for servers.
Problem Statements
The secure score in Defender for Cloud shows that all the virtual machines generate the following recommendation-. Machines should have a vulnerability assessment solution.
All the virtual machines must be compliant in Defender for Cloud.
ClaimApp Deployment
Fabrikam plans to implement an internet-accessible application named ClaimsApp that will have the following specification
* ClaimsApp will be deployed to Azure App Service instances that connect to Vnetl and Vnet2.
* Users will connect to ClaimsApp by using a URL of https://claims.fabrikam.com.
* ClaimsApp will access data in ClaimsDB.
* ClaimsDB must be accessible only from Azure virtual networks.
* The app services permission for ClaimsApp must be assigned to ClaimsDB.
Application Development Requirements
Fabrikam identifies the following requirements for application development:
* Azure DevTest labs will be used by developers for testing.
* All the application code must be stored in GitHub Enterprise.
* Azure Pipelines will be used to manage application deployments.
* All application code changes must be scanned for security vulnerabilities, including application code or configuration files that contain secrets in clear text. Scanning must be done at the time the code is pushed to a repository.
Security Requirement
Fabrikam identifies the following security requirements:
* Internet-accessible applications must prevent connections that originate in North Korea.
* Only members of a group named InfraSec must be allowed to configure network security groups (NSGs} and instances of Azure Firewall, VJM. And Front Door in Sub1.
* Administrators must connect to a secure host to perform any remote administration of the virtual machines. The secure host must be provisioned from a custom operating system image.
AWS Requirements
Fabrikam identifies the following security requirements for the data hosted in ContosoAWSV.
* Notify security administrators at Fabrikam if any AWS EC2 instances are noncompliant with secure score recommendations.
* Ensure that the security administrators can query AWS service logs directly from the Azure environment.
Contoso Developer Requirements
Fabrikam identifies the following requirements for the Contoso developers;
* Every month, the membership of the ContosoDevelopers group must be verified.
* The Contoso developers must use their existing contoso.onmicrosoft.com credentials to access the resources in Sub1.
* The Comoro developers must be prevented from viewing the data in a column named MedicalHistory in the ClaimDetails table.
Compliance Requirement
Fabrikam wants to automatically remediate the virtual machines in Sub1 to be compliant with the HIPPA HITRUST standard. The virtual machines in TestRG must be excluded from the compliance assessment.
NEW QUESTION # 131
You open Microsoft Defender for Cloud as shown in the following exhibit.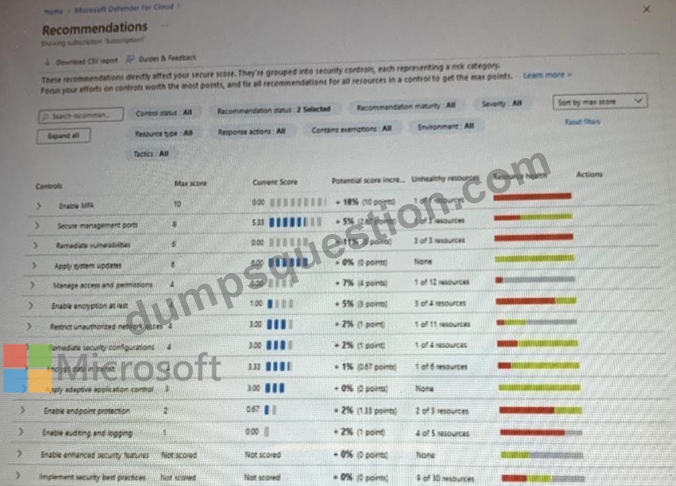
Use the drop-down menus to select the answer choice that complete each statements based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.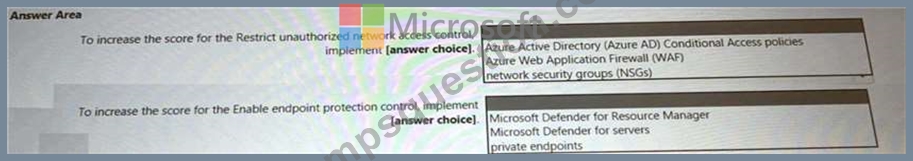
Answer:
Explanation: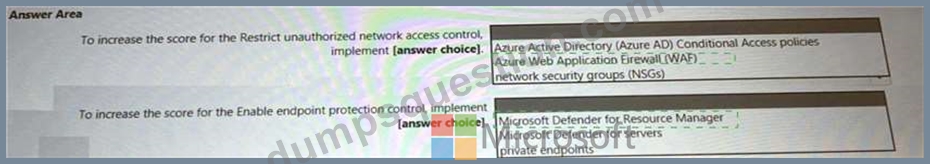
NEW QUESTION # 132
Your on-premises network contains an e-commerce web app that was developed in Angular and Nodejs. The web app uses a MongoDB database. You plan to migrate the web app to Azure. The solution architecture team proposes the following architecture as an Azure landing zone.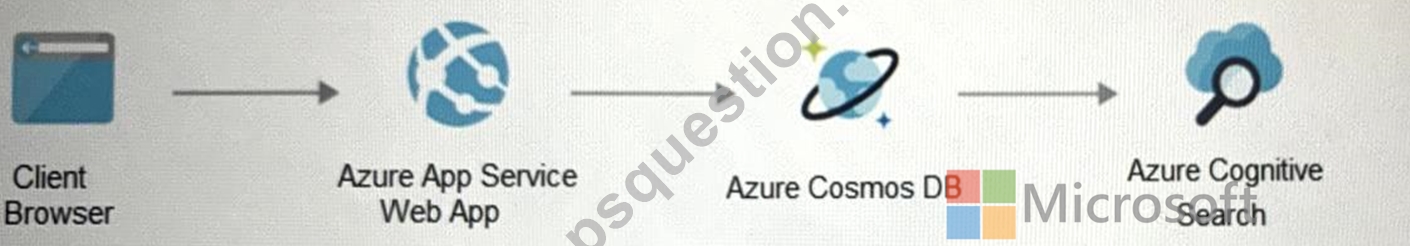
You need to provide recommendations to secure the connection between the web app and the database. The solution must follow the Zero Trust model.
Solution: You recommend creating private endpoints for the web app and the database layer.
Does this meet the goal?
- A. Yes
- B. No
Answer: A
NEW QUESTION # 133
Your company has a hybrid cloud infrastructure.
Data and applications are moved regularly between cloud environments.
The company's on-premises network is managed as shown in the following exhibit.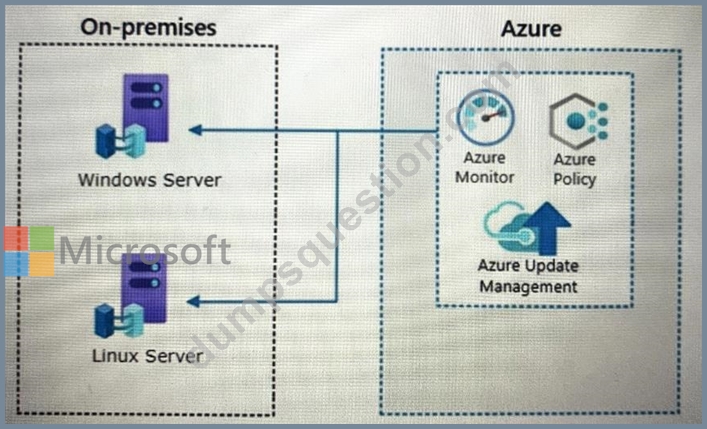
NOTE Each correct selection is worth one point.
- A. on-premises data gateway
- B. Azure VPN Gateway
- C. Azure Arc
- D. guest configuration in Azure Policy
- E. Azure Bastion
Answer: A,C
NEW QUESTION # 134
You have a multi-cloud environment that contains an Azure subscription and an Amazon Web Services (AWS) account.
You need to implement security services in Azure to manage the resources in both subscriptions. The solution must meet the following requirements:
* Automatically identify threats found in AWS CloudTrail events.
* Enforce security settings on AWS virtual machines by using Azure policies.
What should you include in the solution for each requirement? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.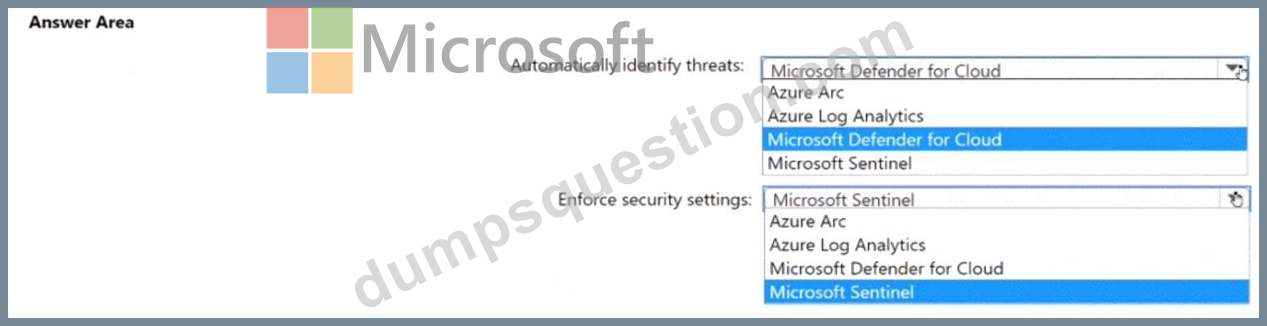
Answer:
Explanation: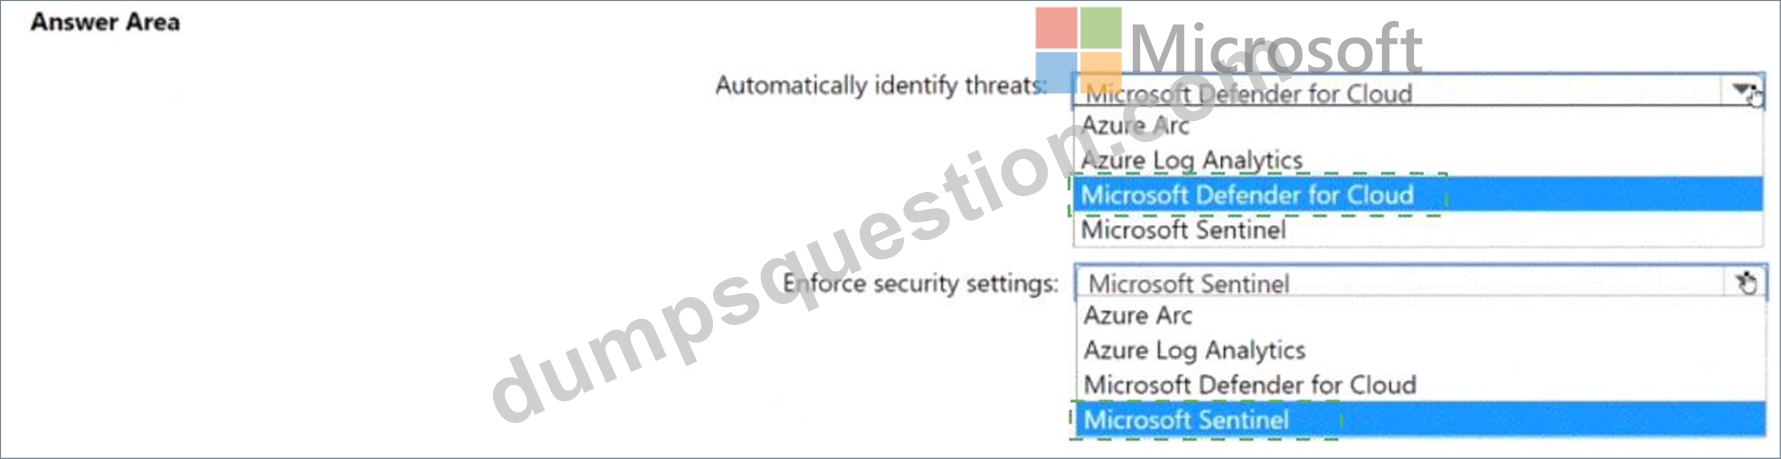
Explanation: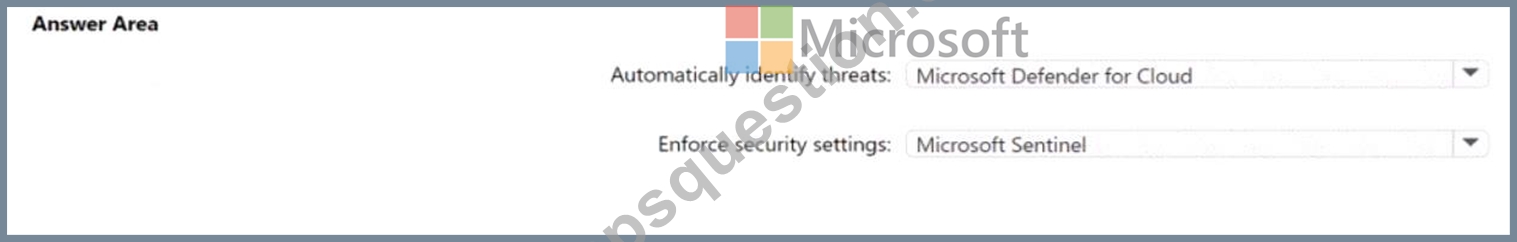
NEW QUESTION # 135
Hotspot Question
You have 1,000 on-premises servers that run Linux.
You have an Azure subscription that contains a Microsoft Sentinel workspace named WS1 and
1,000 virtual machines that run Linux.
All the on-premises Linux servers are onboarded to Azure Arc.
You plan to collect Common Event Format (CEF) logs by using the Azure Monitor Agent connector in Microsoft Sentinel.
You need to design a solution for collecting specific events from the logs. The solution must meet the following requirements:
- Minimize the number of Microsoft Entra ID identities required.
- Minimize the number of events delivered to WS1.
- Ensure that all the required events are ingested.
- Minimize administrative effort.
What should you include in the solution? To answer, select the options in the answer area.
NOTE: Each correct answer is worth one point.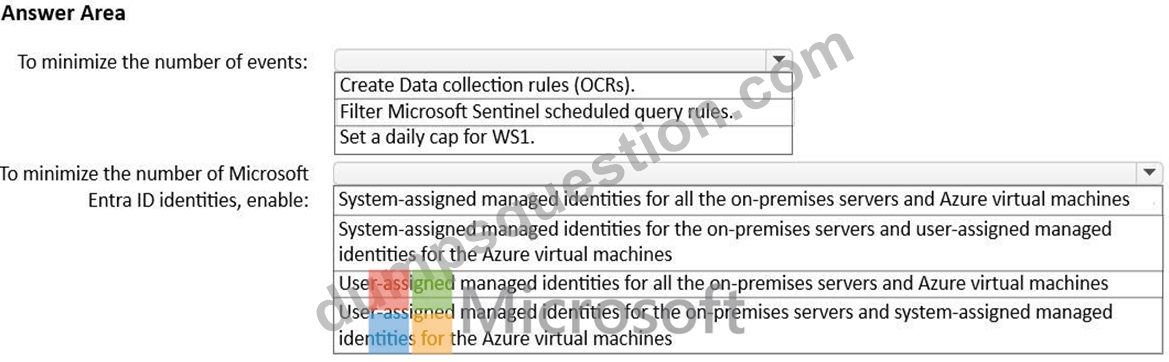
Answer:
Explanation: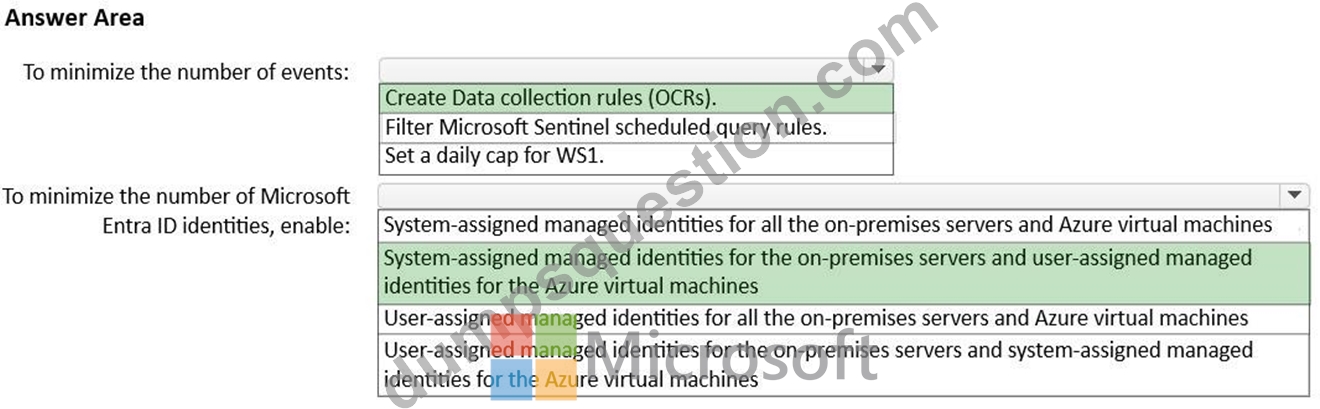
Explanation:
Box 1: Create Data collection rules (OCRs)
Minimize the number of events delivered to WS1.
Ingest syslog and CEF messages to Microsoft Sentinel with the Azure Monitor Agent Use the Syslog via AMA and Common Event Format (CEF) via AMA connectors to quickly filter and ingest syslog messages, including messages in Common Event Format (CEF), from Linux machines and from network and security devices and appliances.
Create data collection rule (DCR)
To get started, open either the Syslog via AMA or Common Event Format (CEF) via AMA data connector in Microsoft Sentinel and create a data collection rule (DCR).
Note: See step 10 below.
1. For Microsoft Sentinel in the Azure portal, under Configuration, select Data connectors. For Microsoft Sentinel in the Defender portal, select Microsoft Sentinel > Configuration > Data connectors.
2. For syslog, type Syslog in the Search box. From the results, select the Syslog via AMA connector. For CEF, type CEF in the Search box. From the results, select the Common Event Format (CEF) via AMA connector.
3. Select Open connector page on the details pane.
4. In the Configuration area, select +Create data collection rule.
5. In the Basic tab:
Type a DCR name.
Select your subscription.
Select the resource group where you want to locate your DCR.
6. Select Next: Resources >.
7. Use the available filters or search box to find your log forwarder VM. Expand a subscription in the list to see its resource groups, and a resource group to see its VMs.
8. Select the log forwarder VM that you want to install the AMA on. The check box appears next to the VM name when you hover over it.
9. Select the log forwarder VM that you want to install the AMA on. The check box appears next to the VM name when you hover over it.
*-> 10. In the Collect tab, select the minimum log level for each facility. When you select a log level, Microsoft Sentinel collects logs for the selected level and other levels with higher severity.
For example, if you select LOG_ERR, Microsoft Sentinel collects logs for the LOG_ERR, LOG_CRIT, LOG_ALERT, and LOG_EMERG levels.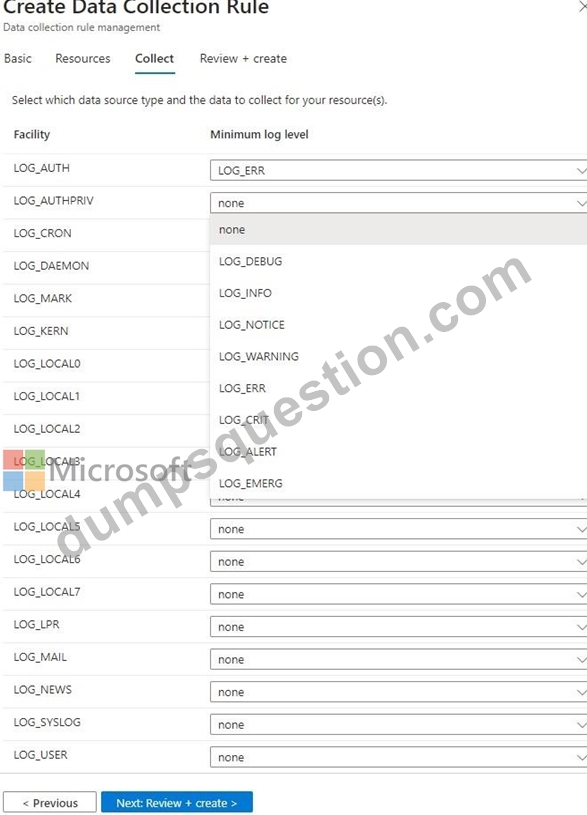
11. Review your selections and select Next: Review + create.
Box 2: System-assigned managed identities for all on-premises servers and uses-assigned managed identities for the Azure virtual machines.
Minimize the number of Microsoft Entra ID identities required.
* On-premises servers
Managed identity
At creation, the Microsoft Entra ID system-assigned identity can only be used to update the status of the Azure Arc-enabled servers, for example, the 'last seen' heartbeat. Grant identity access to Azure resources to enable applications on your server to access Azure resources, for example, to request secrets from a Key Vault.
* Azure virtual machines
User assigned managed identities can be used on more than one resource.
Reference:
https://learn.microsoft.com/en-us/azure/sentinel/connect-cef-syslog-ama
https://learn.microsoft.com/en-us/azure/cloud-adoption-framework/scenarios/hybrid/arc-enabled- servers/eslz-identity-and-access-management
NEW QUESTION # 136
......
View All SC-100 Actual Free Exam Questions Updated: https://www.dumpsquestion.com/SC-100-exam-dumps-collection.html
SC-100 Dumps Updated May 30, 2026 WIith 335 Questions: https://drive.google.com/open?id=1S8a-Ku2I9C8QLtNbv4Bd9BVn18bO9e1b