

Mar-2024 Get Totally Free Updates on SC-400 Dumps PDF Questions
Prepare With Top Rated High-quality SC-400 Dumps For Success in SC-400 Exam
Microsoft SC-400 Exam is designed to assess the ability of candidates to implement and manage Microsoft Information Protection solutions across various Microsoft 365 workloads. It covers a wide range of topics, including data classification, labeling, and protection, data loss prevention, and data governance, among others. It is a comprehensive exam that requires a deep understanding of the Microsoft 365 ecosystem and its various components.
Microsoft SC-400 Exam: Everything You Need to Know
Resourceful Tips to Pass the Microsoft SC-400 Exam
Getting Into The Microsoft SC-400 Certification: Study Guide on how to prepare for the exam and what you should expect
Microsoft Information Protection Administrator Certification is given to individuals who have demonstrated their knowledge in the field. In order to acquire this certification, candidates must pass a test and satisfy other requirements. The certification is not mandatory but can serve as proof that the individual has adequate skills in information protection implementation and administration. The Microsoft SC-400 test is composed of multiple choice questions that are related to the concepts that the candidate should know. These concepts include cryptographic fundamentals; security principles and concepts; security architecture design considerations, such as storage systems, network systems and services; access control; auditing and monitoring; data labeling; data recovery; security policy, planning and management fundamentals; identity management principles; rights management services (RMS); and key technologies for securing business data. The candidate may be required to take an exam from one or all of the above categories. You can check its importance by knowing that most of the MS certified candidates have passed their exams by attempting Microsoft SC-400 exam dumps. Individuals may opt to take the Microsoft SC-400 exam at any of the Pearson VUE test centers across the world for a fee. The Microsoft certification exams are conducted at various times during the year. A candidate can schedule an exam according to his or her convenience by selecting from the available dates and locations.
NEW QUESTION # 74
You plan to implement Microsoft 365 Endpoint data loss prevention (Endpoint DLP).
You need to identify which end user activities can be audited on the endpoints, and which activities can be restricted on the endpoints.
What should you identify for each activity? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation: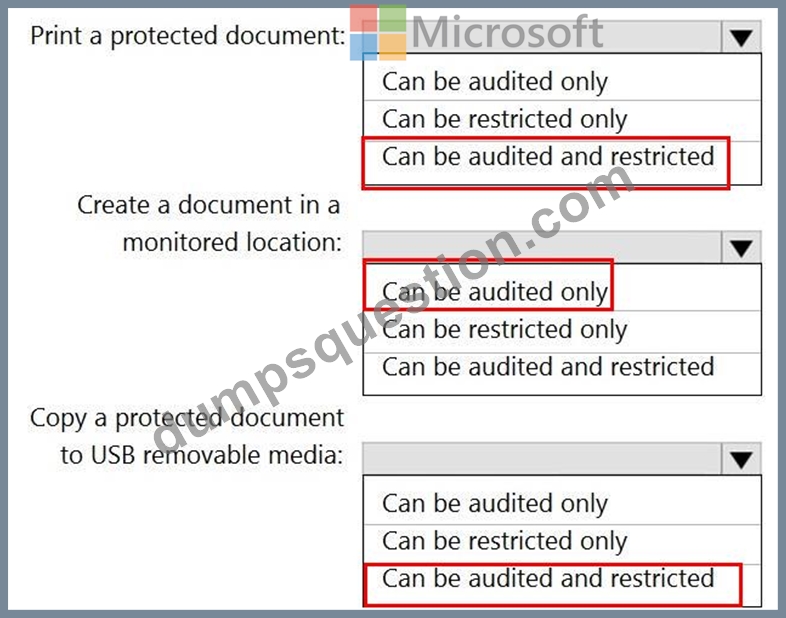
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/endpoint-dlp-learn-about?view=o365-worldwide
NEW QUESTION # 75
You have a Microsoft 365 E5 subscription that contains a security group named Group1 and the users shown in the following table.
You assign the Compliance Manager roles to the users as shown in the following table.
You add two assessments to Compliance Manager as shown in the following exhibit.
For each of the following statements, select Yes if the statement is true. Otherwise, select No. NOTE: Each correct selection is worth one point.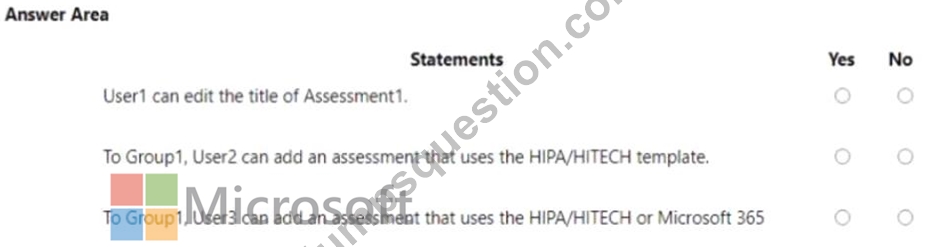
Answer:
Explanation:
Explanation
NEW QUESTION # 76
You need to ensure that documents in a Microsoft SharePoint Online site that contain a reference to Project Alpha are retained for two years, and then deleted.
Which two objects should you create? Each correct answer presents part of the solution. (Choose two.) NOTE: Each correct selection is worth one point.
- A. a sensitive info type
- B. a sensitivity label
- C. a retention label
- D. an auto-apply label policy
- E. a retention policy
- F. a publishing label policy
Answer: C,D
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/apply-retention-labels-automatically?view=o365Wo
NEW QUESTION # 77
You have a Microsoft 365 E5 subscription that contains the users shown in the following table.
You create an assessment named Assesment1 as shown in the following exhibit.
Which users can update the title of Assessment1, and which users can add User5 to the Compliance Manager Readers role group? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
NEW QUESTION # 78
You have a Microsoft 365 tenant that uses data loss prevention (DLP) to protect sensitive information.
You create a new custom sensitive info type that has the matching element shown in the following exhibit.
The supporting elements are configured as shown in the following exhibit.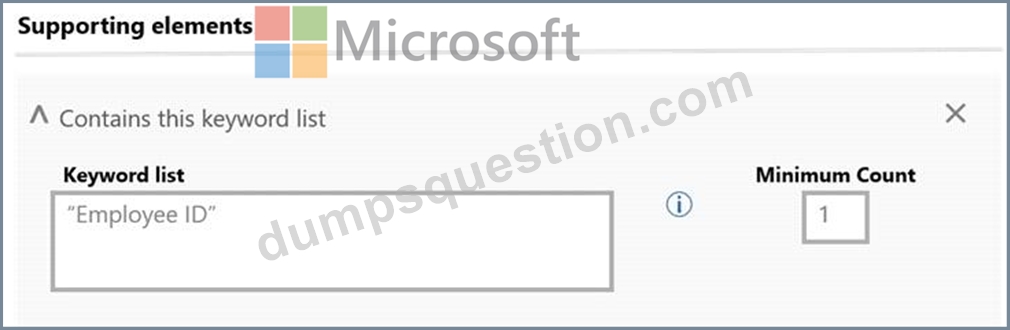
The confidence level and character proximity are configured as shown in the following exhibit.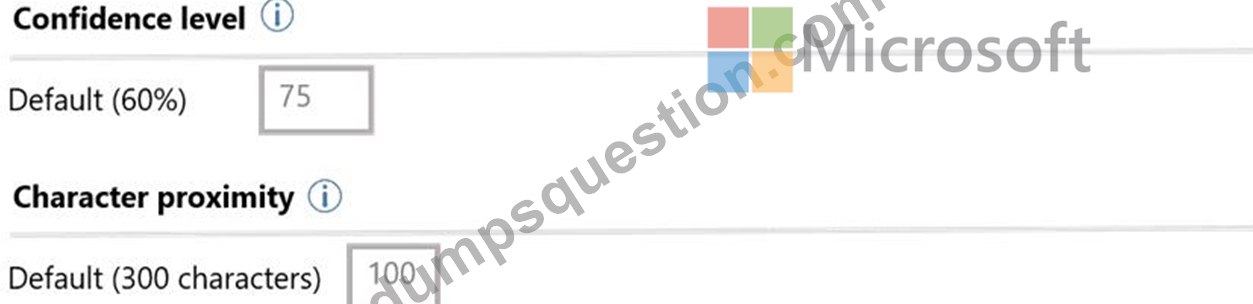
For each of the following statements, select Yes if statement is true. Otherwise, select No NOTE: Each correct selection is worth one point.
Answer:
Explanation: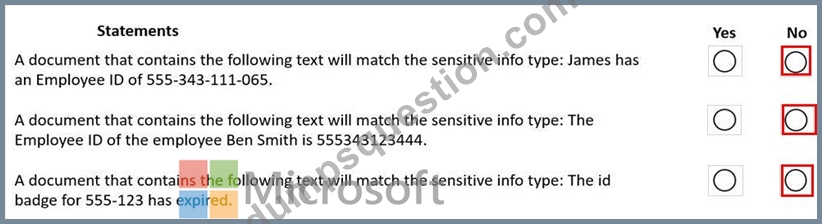
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/create-a-custom-sensitive-information-type?view=o365-worldwide
NEW QUESTION # 79
You need to implement a solution to encrypt email. The solution must meet the compliance requirements.
What should you create in the Exchange admin center and the Microsoft 36.S compliance center? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation: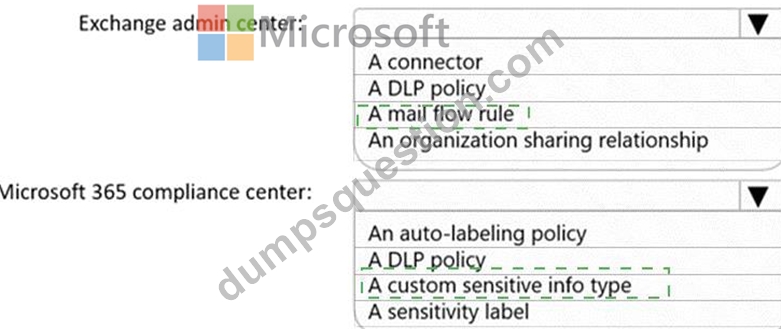
Explanation
Graphical user interface, text, application Description automatically generated
Users must be able to manually select that email messages are sent encrypted. The encryption will use Office
365 Message Encryption (OME) v2. Any email containing an attachment that has the Fabrikam Confidential sensitivity label applied must be encrypted automatically by using OME.
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/ome-sensitive-info-types?view=o365-worldwide
NEW QUESTION # 80
You have a Microsoft 365 E5 tenant.
You need to create a custom trainable classifier that will detect product order forms. The solution must use the principle of least privilege.
What should you do first? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
D:\mudassar\Untitled.jpg
NEW QUESTION # 81
You have the retention label policy shown in the Policy exhibit. (Click the Policy tab.)
Users apply the retention label policy to files and set the asset ID as shown in the following table.
On December 1, 2020, you create the event shown in the Event exhibit. (Click the Event tab.)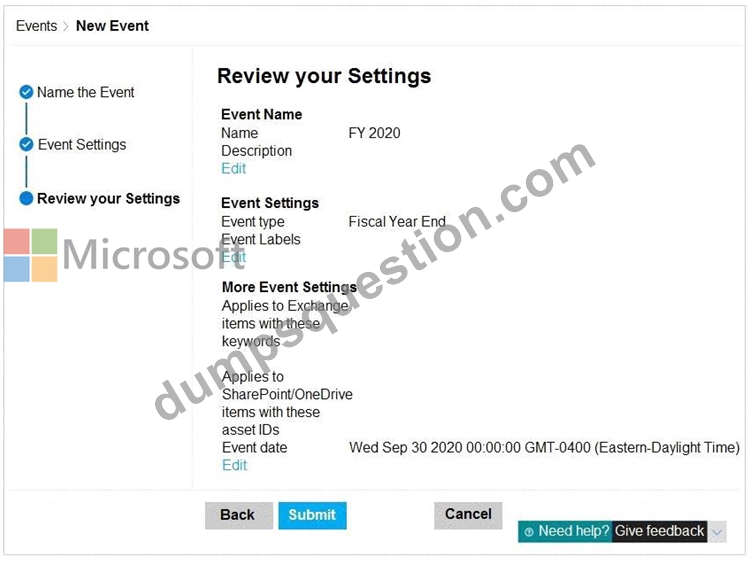
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Graphical user interface, text, application Description automatically generated
NEW QUESTION # 82
You have a data loss prevention (DLP) policy that applies to the Devices location. The policy protects documents that contain States passport numbers.
Users reports that they cannot upload documents to a travel management website because of the policy.
You need to ensure that the users can upload the documents to the travel management website. The solution must prevent the protected content from being uploaded to other locations.
Which Microsoft 365 Endpoint data loss prevention (Endpoint DLP) setting should you configure?
- A. Service domains
- B. Unallowed browsers
- C. Unallowed apps
- D. File path exclusions
Answer: A
Explanation:
Explanation
You can control whether sensitive files protected by your policies can be uploaded to specific service domains from Microsoft Edge.
* If the list mode is set to Block, then user will not be able to upload sensitive items to those domains.
When an upload action is blocked because an item matches a DLP policy, DLP will either generate a
* warning or block the upload of the sensitive item.
* If the list mode is set to Allow, then users will be able to upload sensitive items only to those domains, and upload access to all other domains is not allowed.
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/endpoint-dlp-using?view=o365-worldwide
NEW QUESTION # 83
You have a data loss prevention (DLP) policy that has the advanced DLP rules shown in the following table.
You need to identify which rules will apply when content matches multiple advanced DLP rules.
Which rules should you identify? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/data-loss-prevention-policies?view=o365-worldwide
NEW QUESTION # 84
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You are configuring a file policy in Microsoft Cloud App Security.
You need to configure the policy to apply to all files. Alerts must be sent to every file owner who is affected by the policy. The policy must scan for credit card numbers, and alerts must be sent to the Microsoft Teams site of the affected department.
Solution: You use the Built-in DLP inspection method and send alerts as email.
Does this meet the goal?
- A. No
- B. Yes
Answer: A
Explanation:
Alerts must be sent to the Microsoft Teams site of the affected department. A Microsoft Power Automate playbook should be used.
Reference:
https://docs.microsoft.com/en-us/cloud-app-security/content-inspection-built-in
https://docs.microsoft.com/en-us/cloud-app-security/flow-integration
NEW QUESTION # 85
You have a Microsoft 365 E5 tenant.
You create sensitivity labels as shown in the Sensitivity Labels exhibit.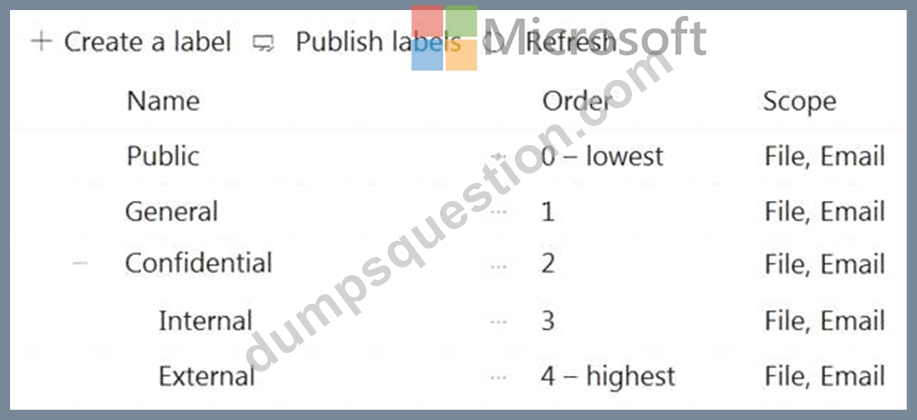
The Confidential/External sensitivity label is configured to encrypt files and emails when applied to content.
The sensitivity labels are published as shown in the Published exhibit.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.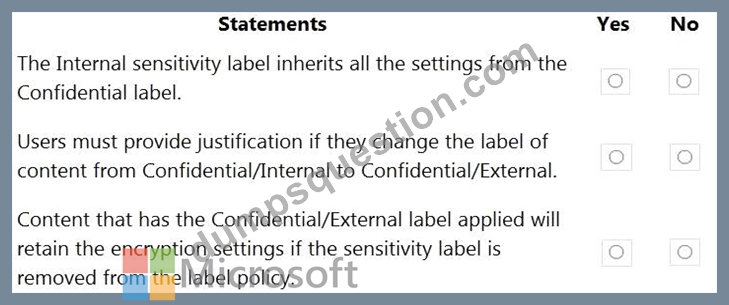
Answer:
Explanation:
Explanation
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/sensitivity-labels?view=o365-worldwide
NEW QUESTION # 86
You have the retention label policy shown in the Policy exhibit. (Click the Policy tab.)
Users apply the retention label policy to files and set the asset ID as shown in the following table.
On December 1, 2020, you create the event shown in the Event exhibit. (Click the Event tab.)
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 87
You are implementing Microsoft Office 365 Message Encryption (OME) for a Microsoft 365 tenant named contoso.com.
You need to meet the following requirements:
* All email to a domain named fabhkam.com must be encrypted automatically.
* Encrypted emails must expire seven days after they are sent-
What should you configure for each requirement? To answer, select the appropriate options NOTE: Each correct selection is worth one point.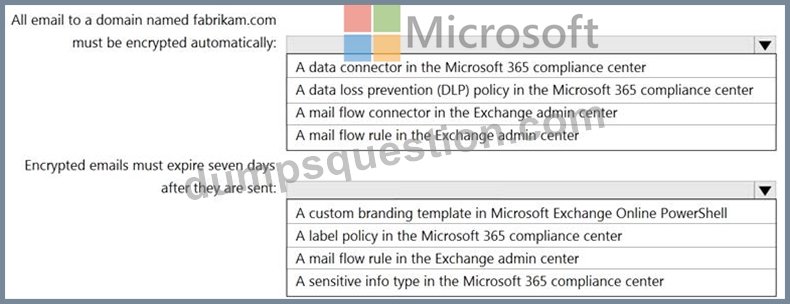
Answer:
Explanation: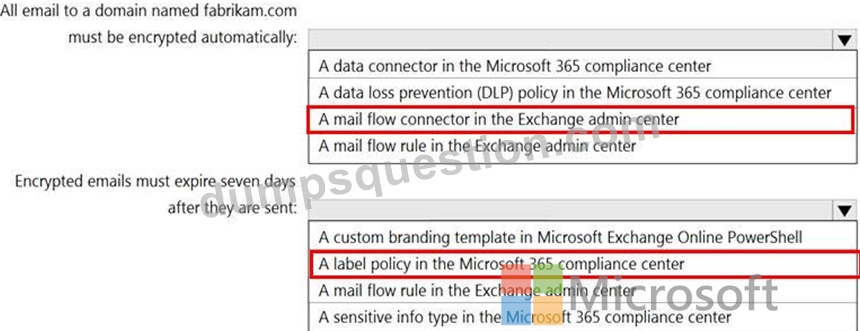
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/email-encryption?view=o365-worldwide
https://docs.microsoft.com/en-us/microsoft-365/compliance/ome-advanced-expiration?view=o365-worldwide
NEW QUESTION # 88
You have a Microsoft 365 E5 tenant that contains a sensitivity label named label1.
You plan to enable co-authoring for encrypted files.
You need to ensure that files that have label1 applied support co-authoring.
Which two settings should you modify? To answer, select the settings in the answer area.
NOTE: Each correct selection is worth one point.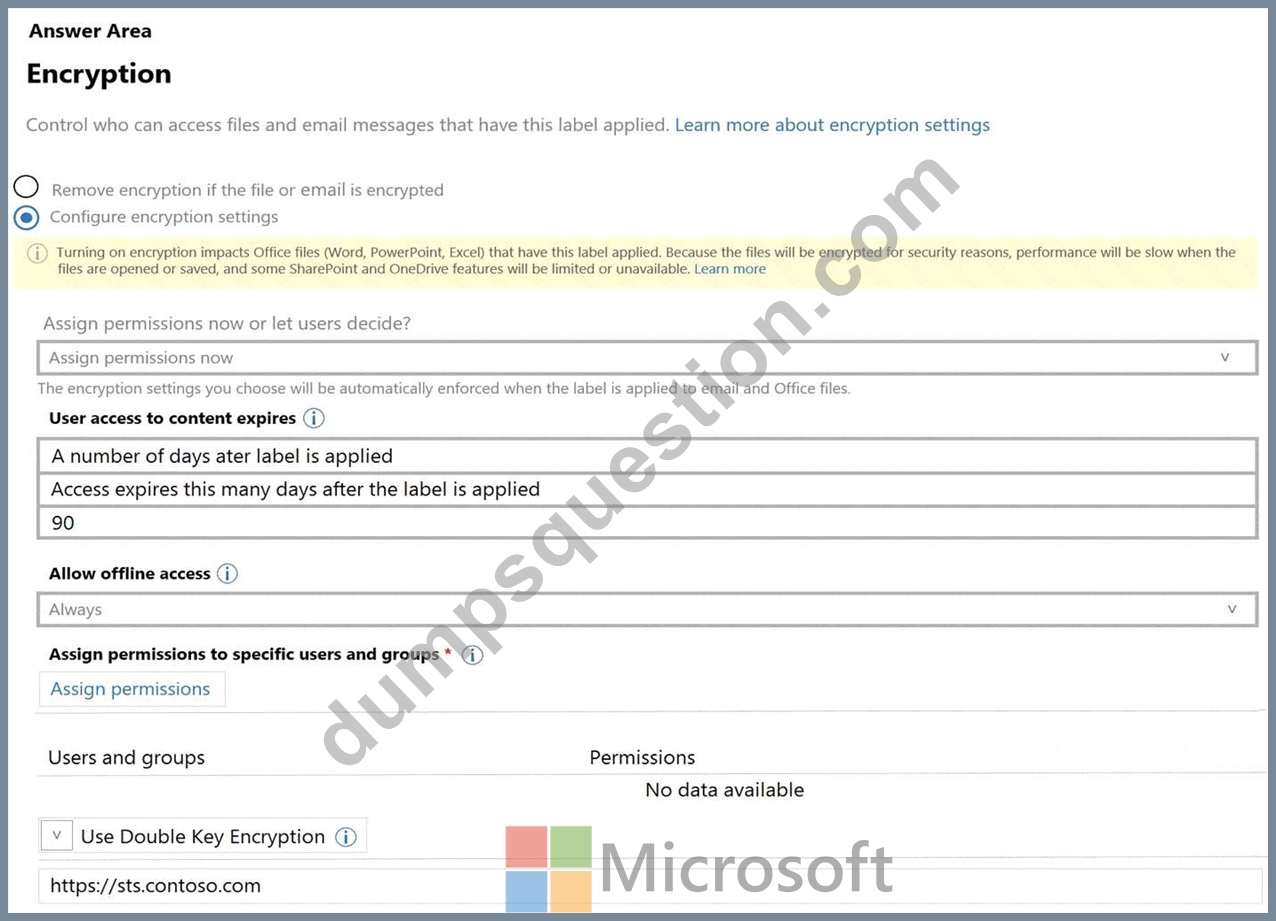
Answer:
Explanation:
Explanation
Graphical user interface, text, application, email Description automatically generated
Co-authoring and AutoSave aren't supported and don't work for labeled and encrypted Office documents that use any of the following configurations for encryption:
Let users assign permissions when they apply the label and the checkbox In Word, PowerPoint, and Excel, prompt users to specify permissions is selected. This configuration is sometimes referred to as
"user-defined permissions".
User access to content expires is set to a value other than Never.
Double Key Encryption is selected.
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/sensitivity-labels-coauthoring?view=o365-worldwid
https://techcommunity.microsoft.com/t5/security-compliance-and-identity/co-authoring-files-with-sensitivity-lab
NEW QUESTION # 89
......
Get 100% Success with Latest Microsoft Certified: Information Protection Administrator Associate SC-400 Exam Dumps: https://www.dumpsquestion.com/SC-400-exam-dumps-collection.html
SC-400 Free Certification Exam Easy to Download PDF Format 2024: https://drive.google.com/open?id=1MONtEqFvGHWLjGWoR-ARvGCWHymTTVYt